This federal contractor struggled with legacy high-end equipment and OT devices that were too fragile to actively scan or patch. Competitors only provided theoretical vulnerability lists, which were operationally useless for them. They deployed Asimily to non-disruptively map their network and go beyond basic CVSS scores using ATT&CK Analysis. By incorporating custom impact factors like safety and downtime, the security team generated zero-trust microsegmentation policies and precise ACLs to isolate unpatchable assets without ripping and replacing legacy systems.
Best-in-Class Security Without Operational Downtime
IoT and OT Security for Government Agencies
Government agencies run critical infrastructure, operations centers, and networks holding thousands of legacy devices, many of which predate modern security capabilities. Asimily takes you from an incomplete device inventory to enforced, auditable policy across operational networks and facilities.
Request a Demo
Threats to government networks come from nation-states, terrorist actors, and opportunistic criminals alike. Mandates including NIST, CISA directives, and FISMA require complete inventory, threat prioritization, and enforced policy, while the operational teams responsible are under-resourced and rightly cautious about change. Asimily’s Proactive Cyber Asset Defense Platform closes the gap between policy requirements and enforced reality. Your existing NAC remains the enforcement point. Asimily supplies the device context, risk prioritization, policy creation, simulation, application, and ongoing maintenance that turn a deployed NAC into operational segmentation across IoT, OT, and IT, without disrupting mission-critical systems.
Request a Demo
Built for Teams That Cannot Afford Downtime
The Trusted Partner for Government Agencies
Few environments are as varied as the public sector: smart cities, large device fleets, wide territories, and obligations such as public safety and open data availability. Asimily is built for that variety, covering IoT, OT, and IT devices on one platform.
Discover All Devices Across Operational Networks
Government networks cross jurisdictions, classifications, and operational zones. Asimily discovers legacy systems, IoT, and modern equipment that individual asset management systems miss, using passive monitoring and active safe scanning where appropriate, so the inventory is complete without a maintenance window.
Prioritize Exploitable Threats, Not Noise
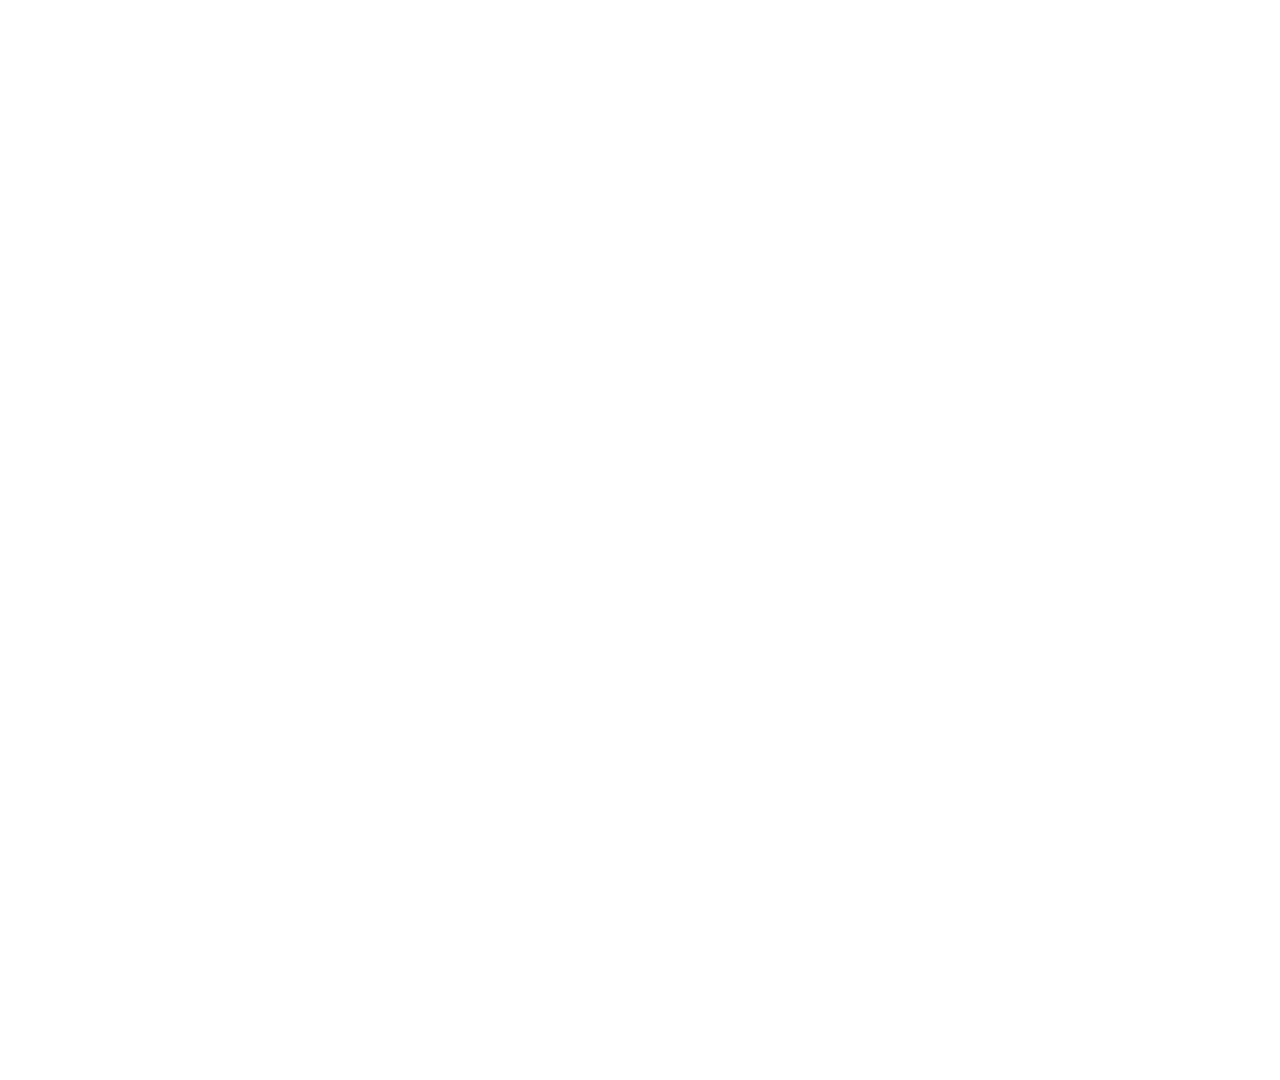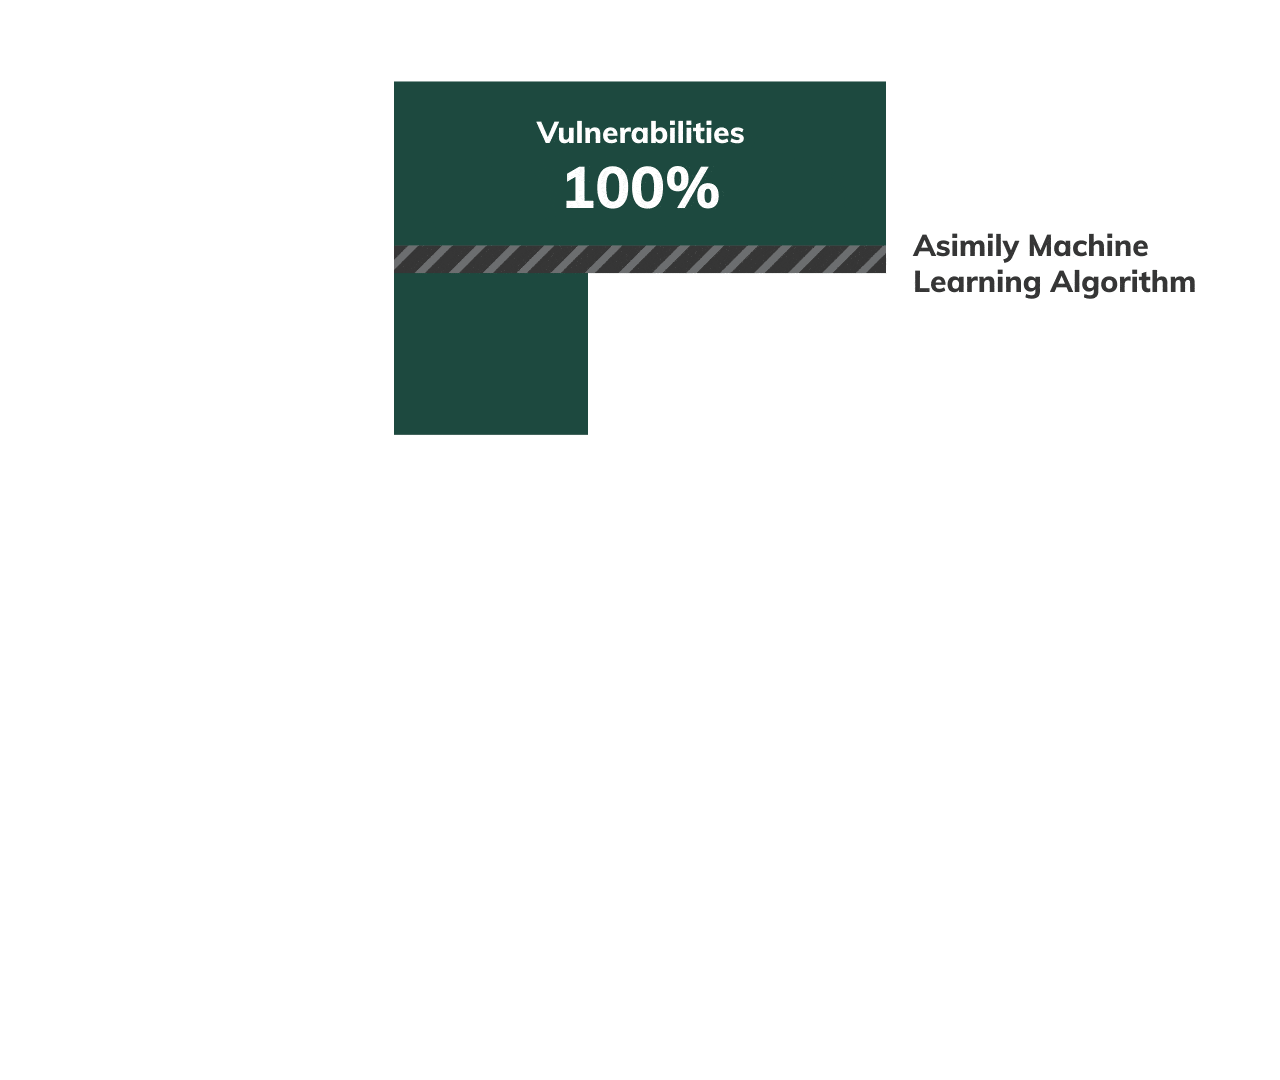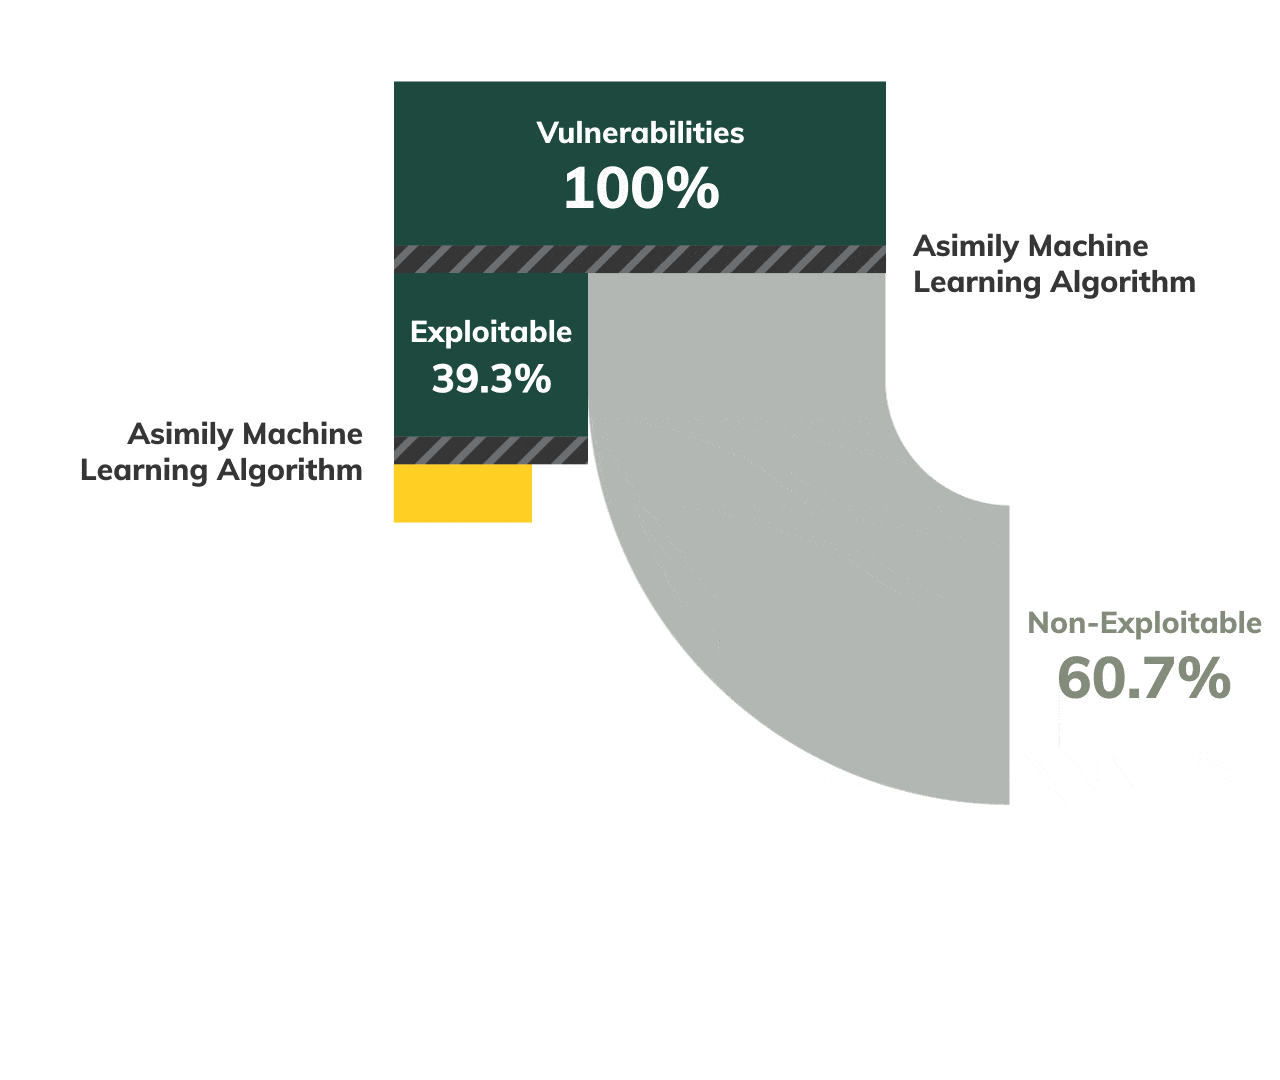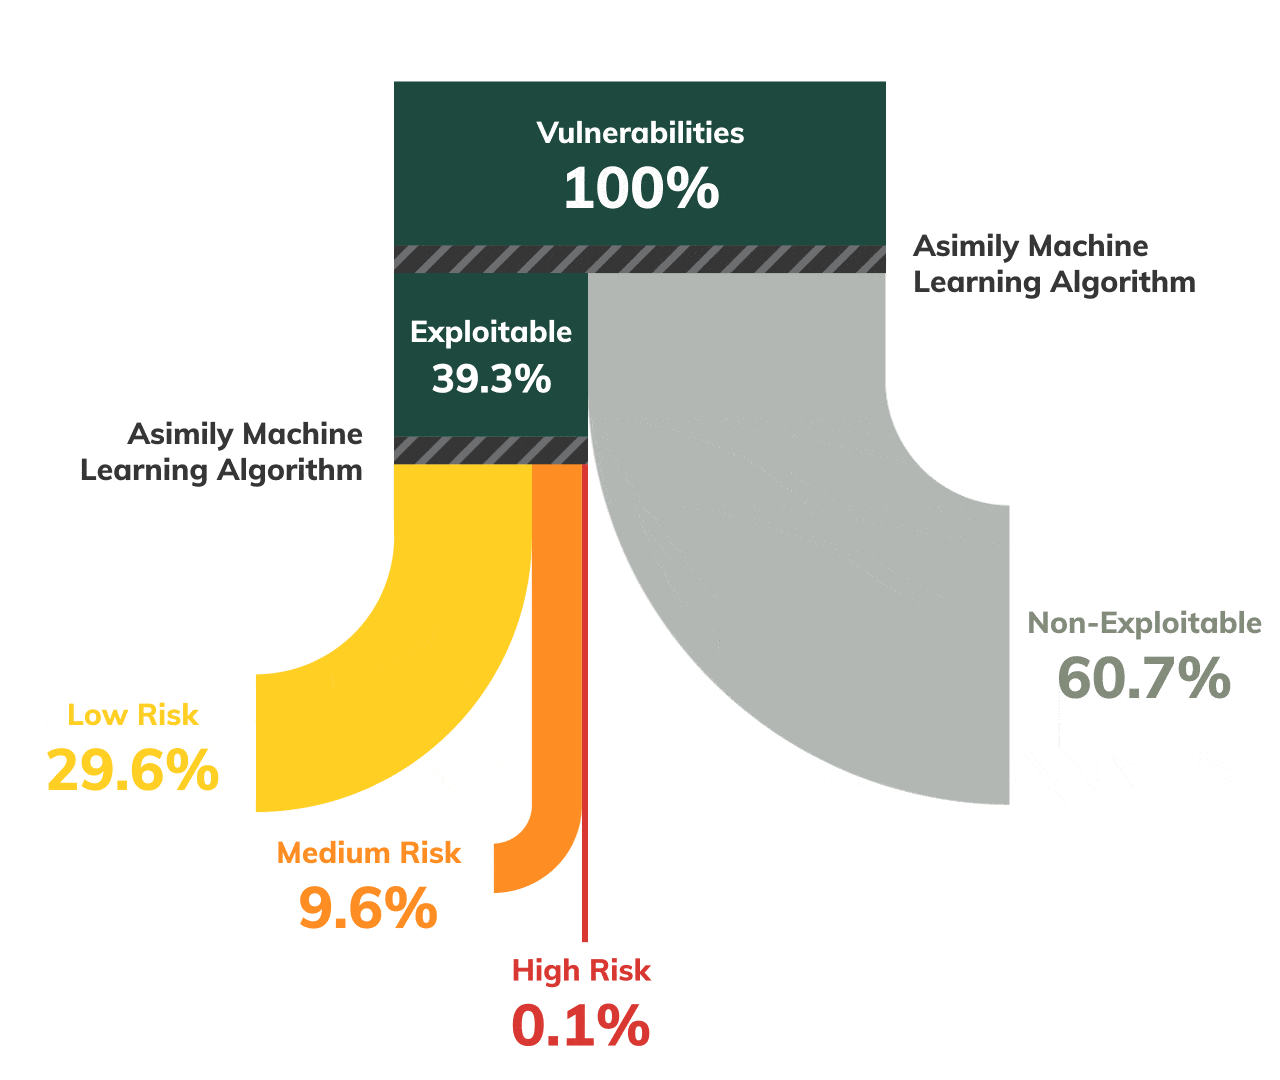
Asimily’s ATT&CK Analysis maps vulnerabilities to your specific devices, topology, and mission context to determine what is genuinely exploitable, so understaffed teams work the threats that could compromise operations rather than the thousands that cannot.
Policies Proven Safe Before You Deploy
Operational teams are cautious about network changes because the cost of getting it wrong falls on them. Policy Simulation runs a proposed policy against real observed traffic and shows exactly which devices and connections would be affected, before anything reaches a production network.
Segmentation at Scale, Kept Current
Most agencies have NAC infrastructure that was never used for much beyond authentication. Segmentation Orchestration generates policies in your NAC’s native format, simulates them, applies them, and maintains them as the network changes, producing a record that is automated, auditable, and protects against the latest exploits.
Reduce IoT Risk in the Public Sector
Compliance Without Gaps
NIST, CISA directives, and FISMA all include similar requirements, starting with a complete device inventory, a defensible risk assessment, and evidence that controls are enforced. Asimily produces the audit trail for all three, including a record of which policies are active on which devices and when they changed.

Spend Time Where It Matters
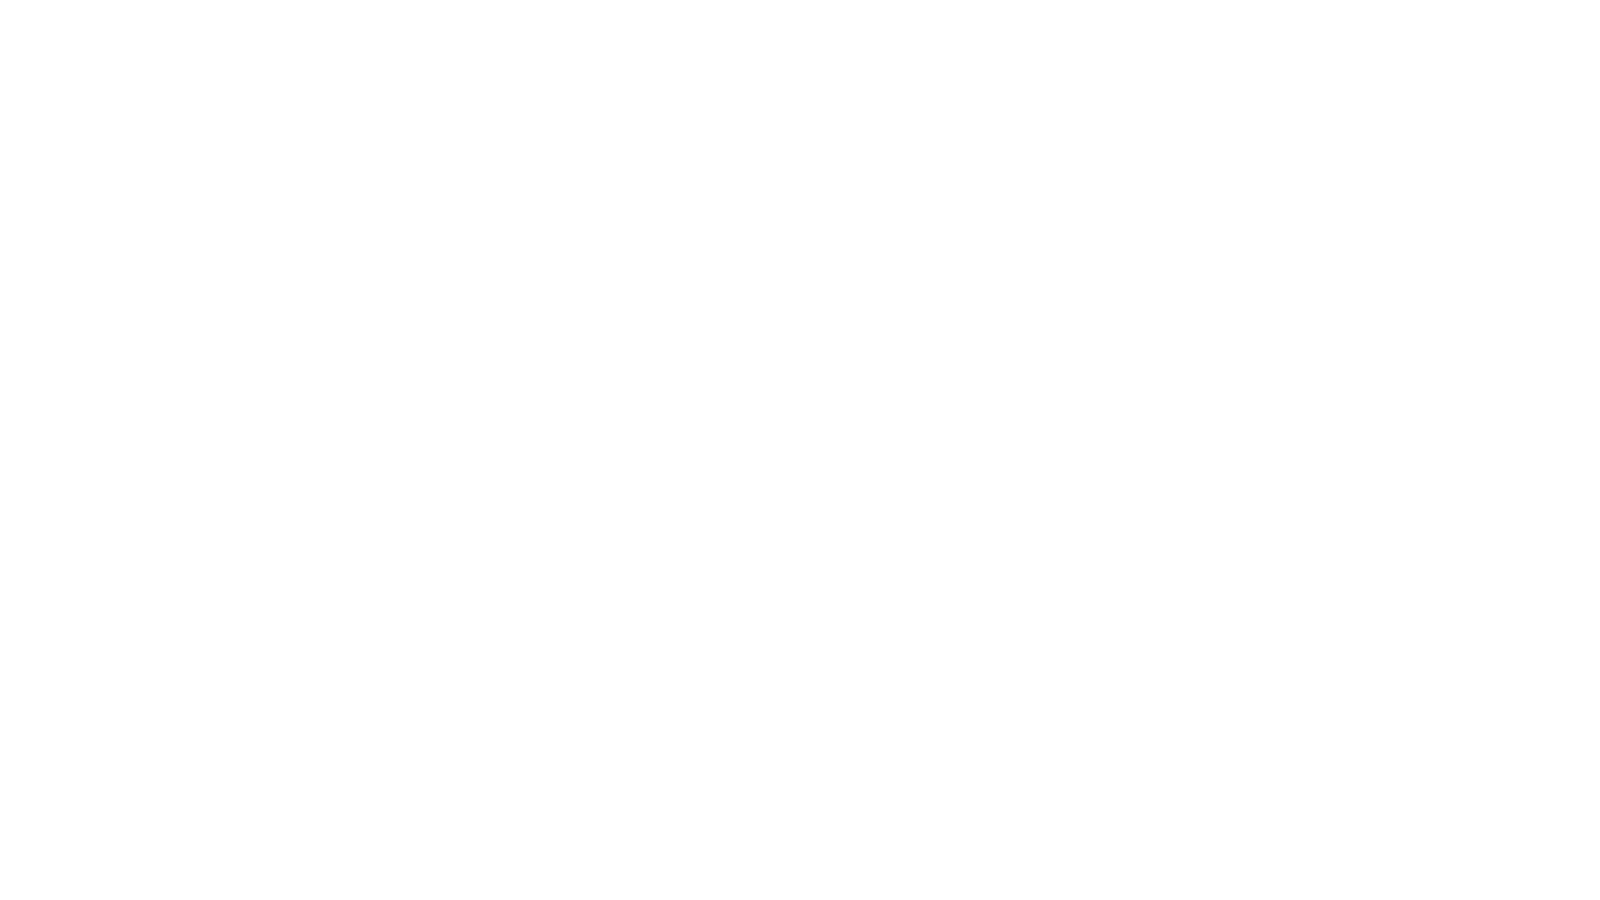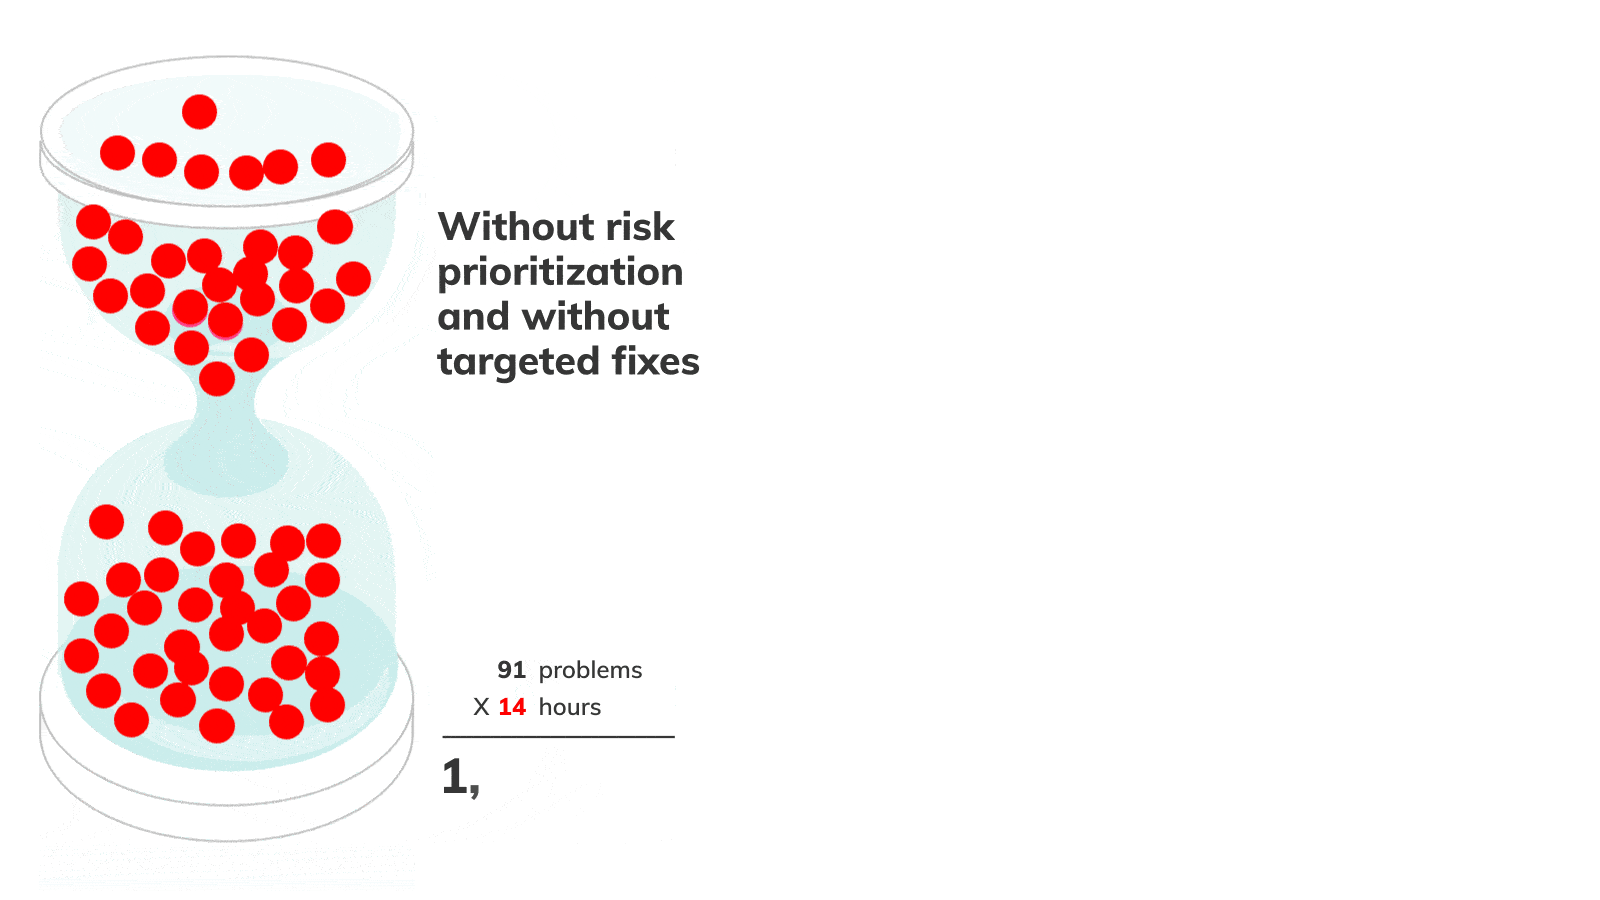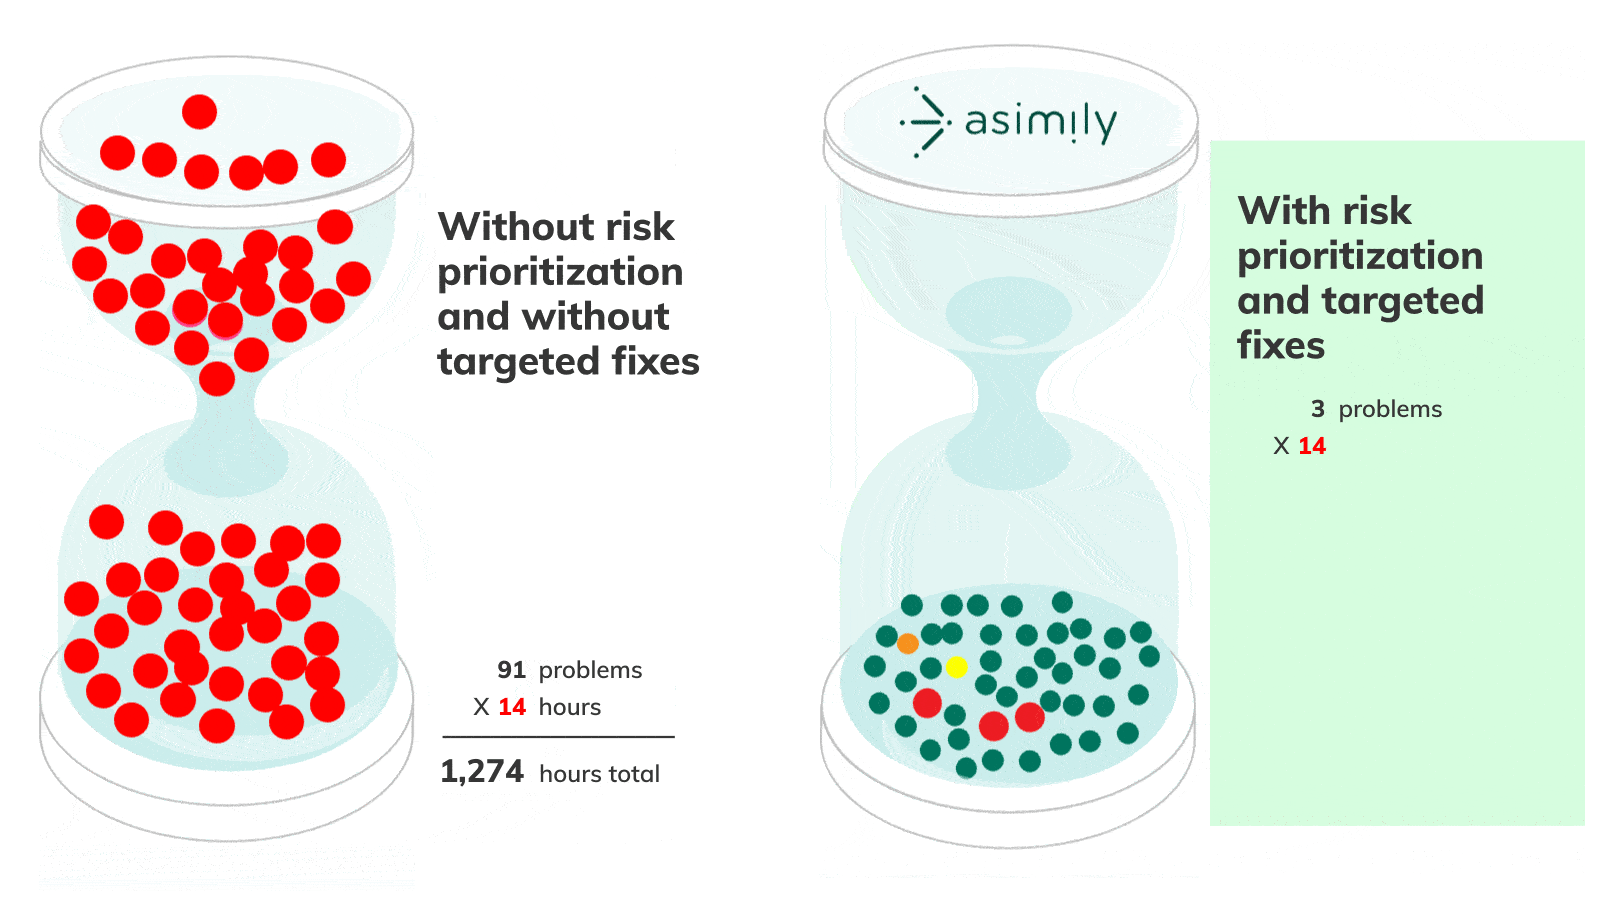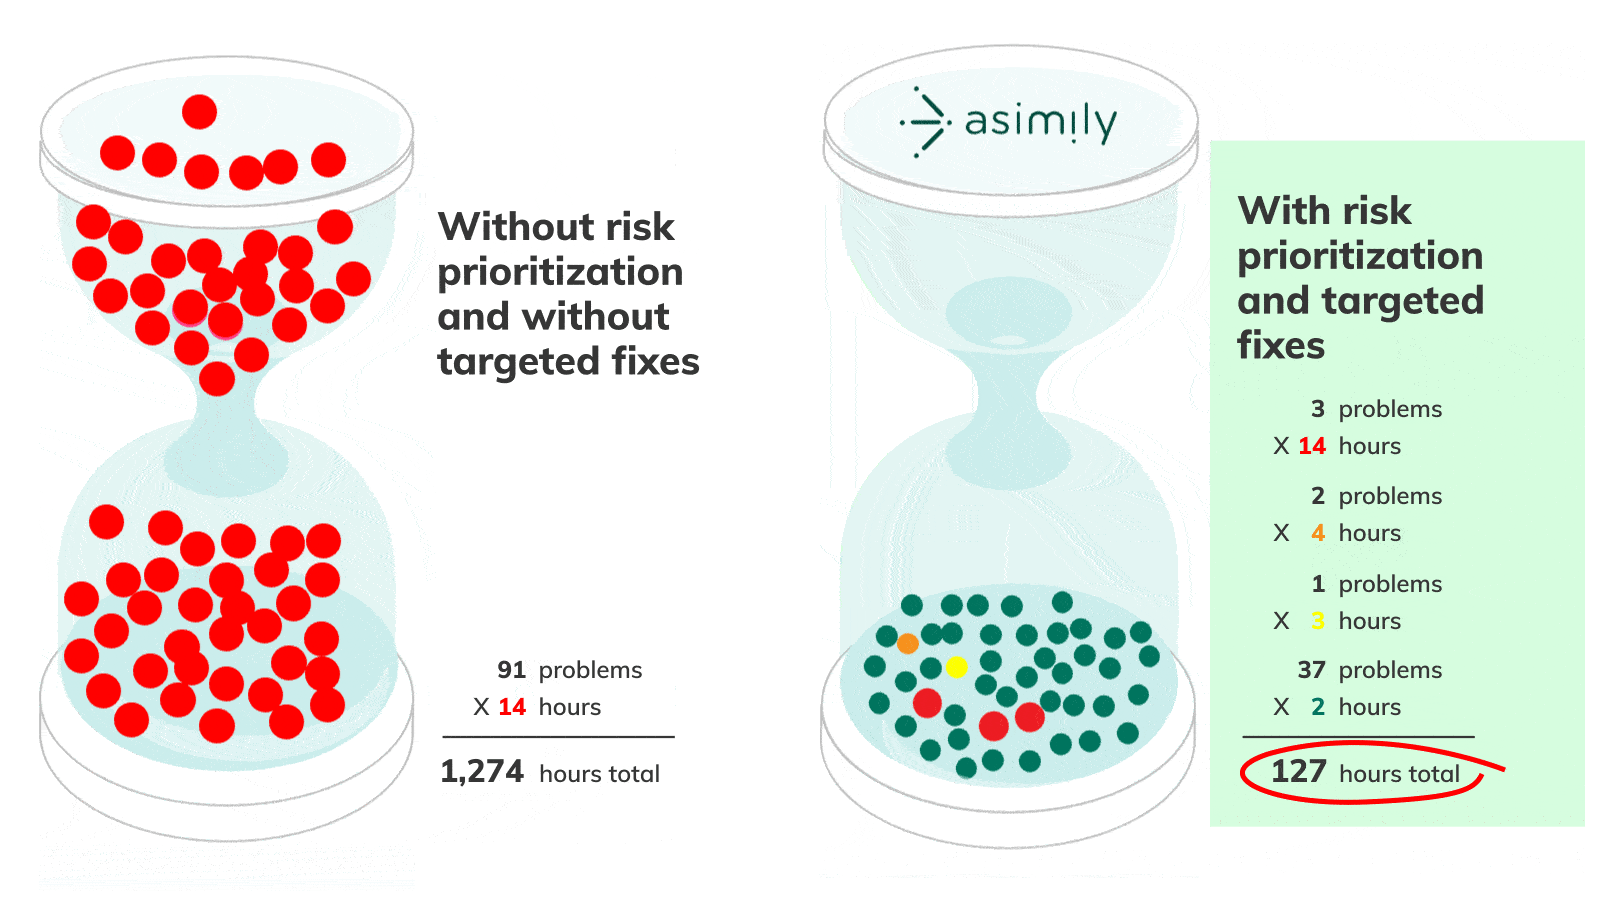
Government security teams are staffed for a fraction of the task queue in front of them. Asimily ranks that queue by real exploitability in your environment and documents the reason for each ranking, so a small team can defend how it spent its time as well as what it fixed.
Options to Mitigate Risk, Fast
Mitigate risk even when legacy OT and IoT in government cannot be patched at all, whether because of warranty terms, certification requirements, or age. Asimily pairs targeted mitigations with segmentation, so risk on those devices comes down without a rip-and-replace program and without waiting on a vendor update that may never arrive.
Secure Every IoT Device.
Automatically.
Cyber threats move fast — so should you. Asimily gives instant inventory and smart, prioritized risk mitigation insights for every IoT, OT, and IoMT device — so you can take action before threats strike.