This bank’s challenge centered on building management OT and a growing fleet of corporate IoT devices. The bank needed to proactively secure those devices, and the vendors they evaluated offered visibility without a way to actively patch or mitigate IoT risk. They deployed Asimily for full visibility, using IoT API querying that returned better device data than passive monitoring alone. They used Asimily’s IoT Patching to remediate vulnerabilities directly on supported device types, a capability that helped set Asimily apart from the competition. The deployment’s results led to Asimily being recommended to, and piloted by, several other banks in the region.
Protect Financial Services Infrastructure Without Disrupting It
IoT and OT Security for Financial Services
Financial institutions run payment terminals, card readers, HVAC controls, and building access systems alongside modern IT, frequently on shared networks. Asimily takes you from a scattered device inventory to enforced, auditable protection across payment systems, branch infrastructure, and data centers.
Request a Demo
Protect Your Entire Attack Surface, Not Just IT
Legacy branch equipment shares networks with modern IT, and mandates including PCI-DSS, SOX, and GLBA require complete visibility and documented proof of control. Most institutions can produce a device list. Far fewer can show an examiner which controls are enforced on which devices, and that enforcement is what audits increasingly turn on. Asimily closes the gap between fragmented visibility and enforced protection. Your existing NAC remains the enforcement point. Asimily supplies the device context, risk prioritization, policy creation, simulation, application, and ongoing maintenance that turn a deployed NAC into operational segmentation across IoT, OT, and IT.
Request a Demo
Stay Ahead of Attackers with Efficient Protection
Security teams in financial services are drowning in alerts. What they need is a defensible way to decide which exposures actually threaten financial processing and customer access, and a safe way to enforce that decision once it is made. Asimily addresses both in one comprehensive exposure management platform.
Full Visibility Across Financial Services Infrastructure
Card readers, ATMs, payment gateways, door controls, environmental sensors, and HVAC systems appear in a single authoritative inventory. Discovery is agentless and safe to run in production, so legacy branch equipment and newer IoT surface without a maintenance window or a change ticket.
Understand Risk in Context
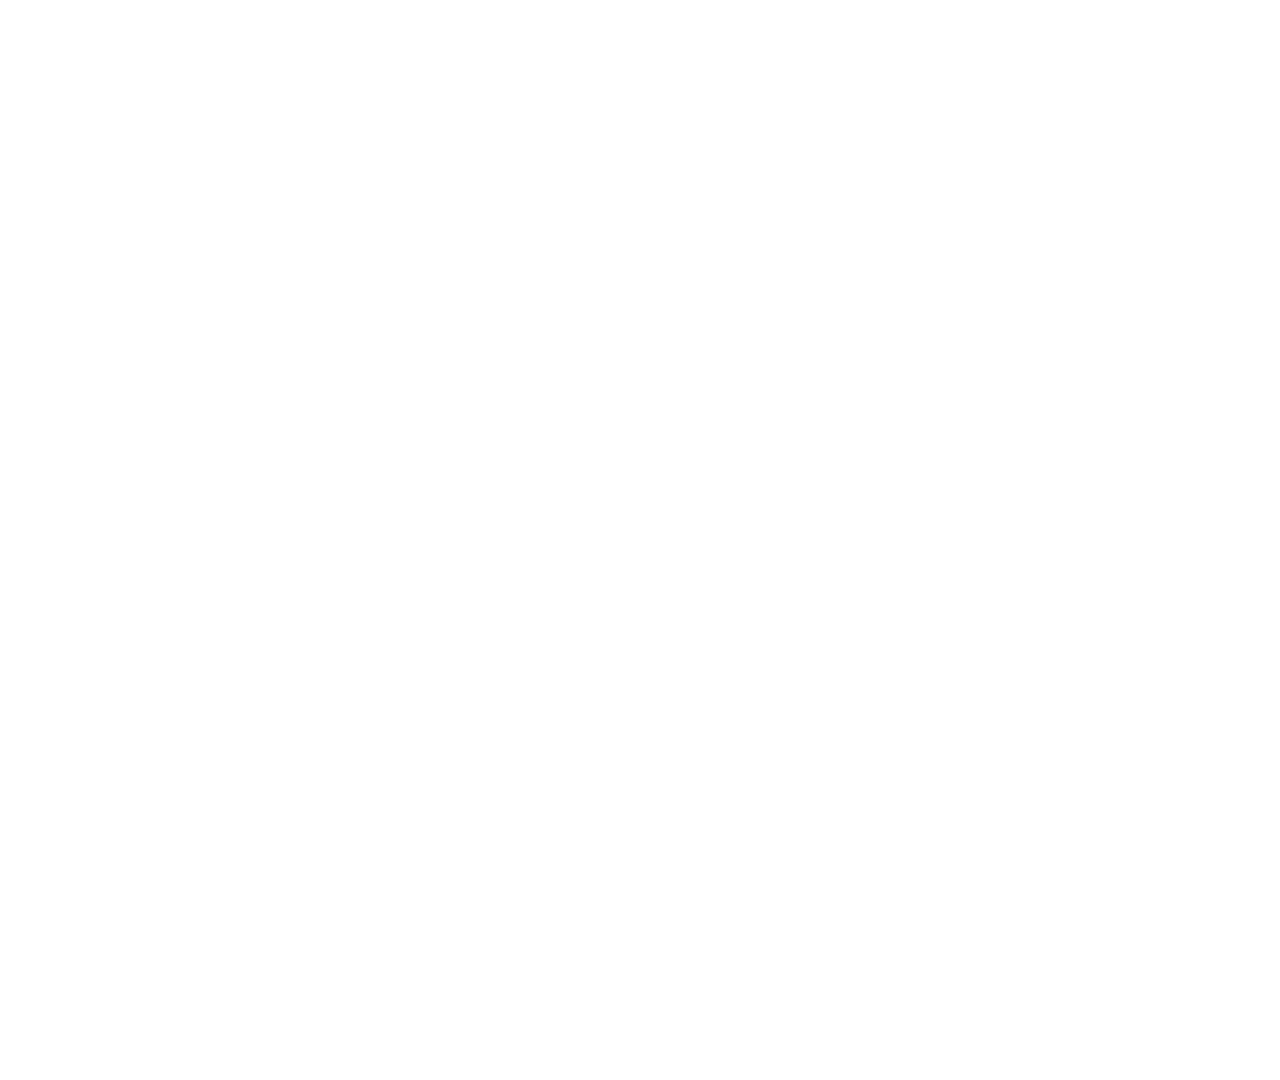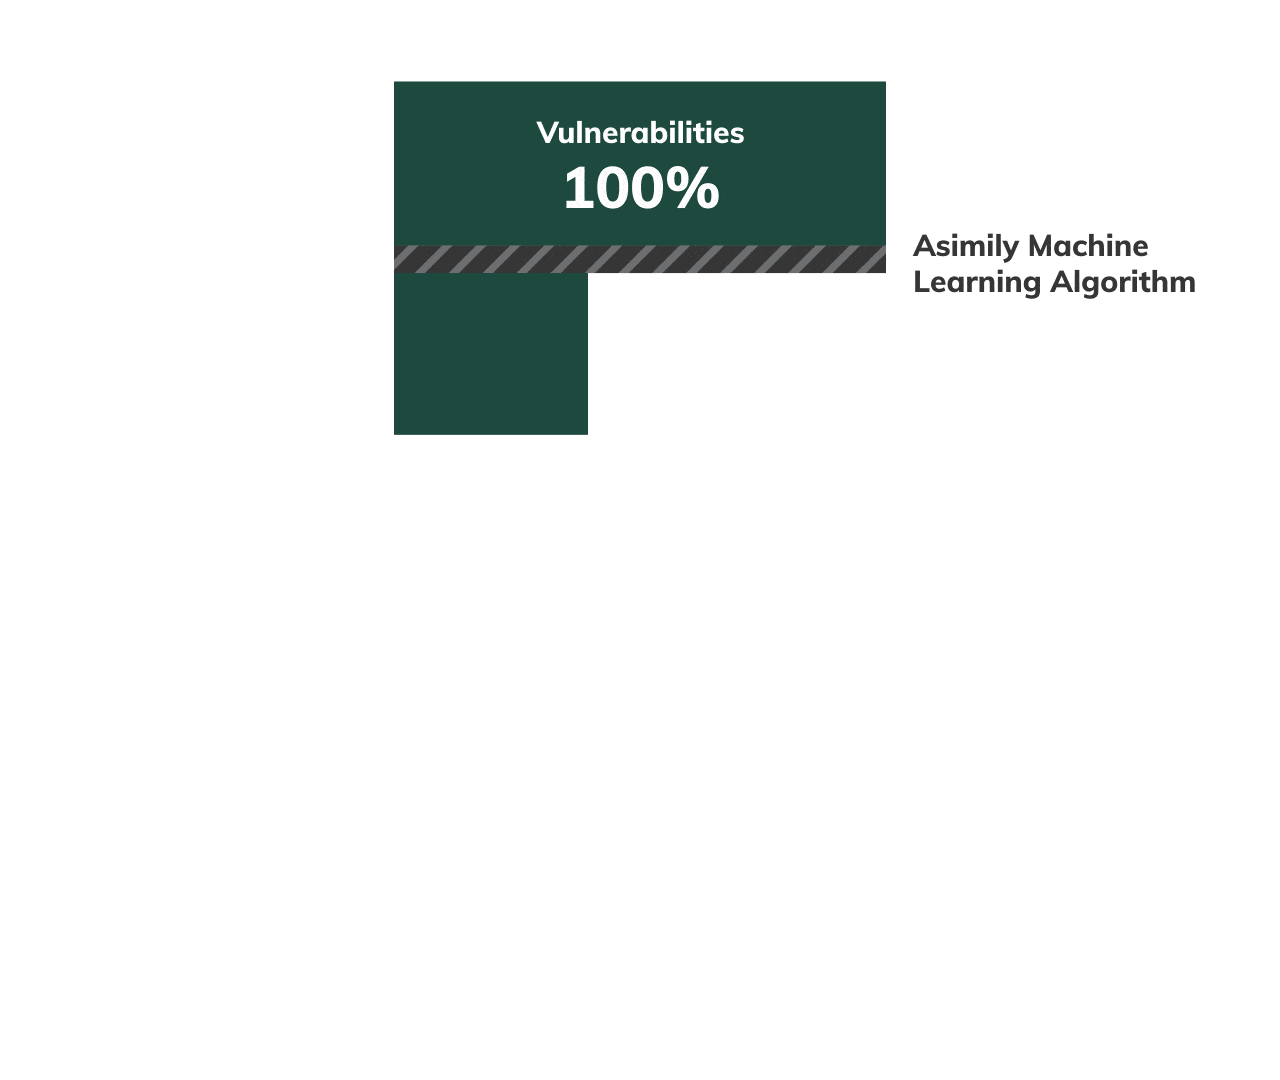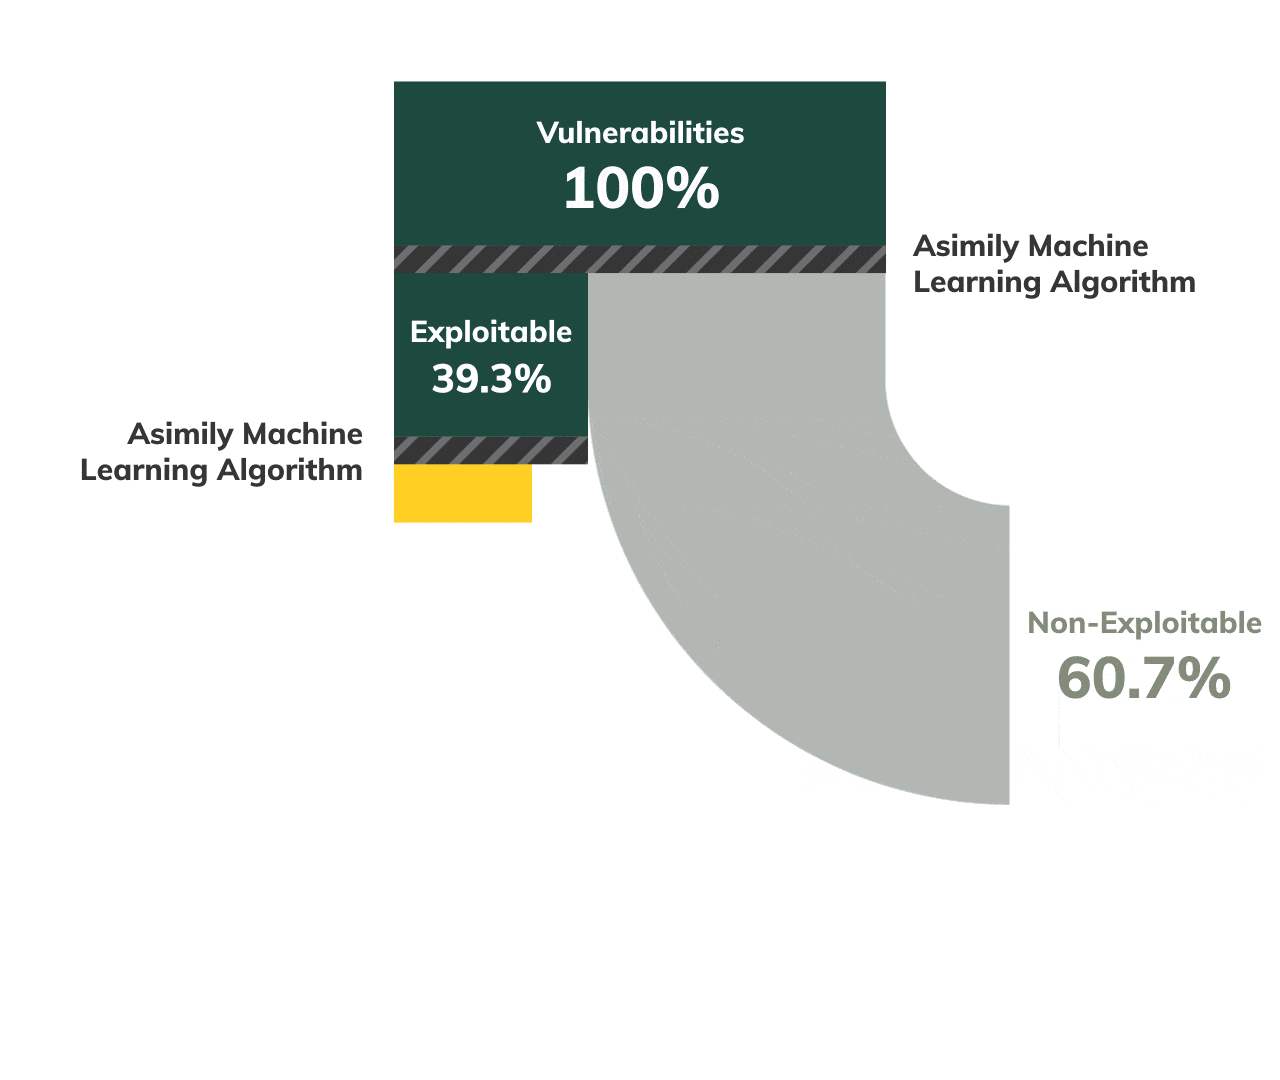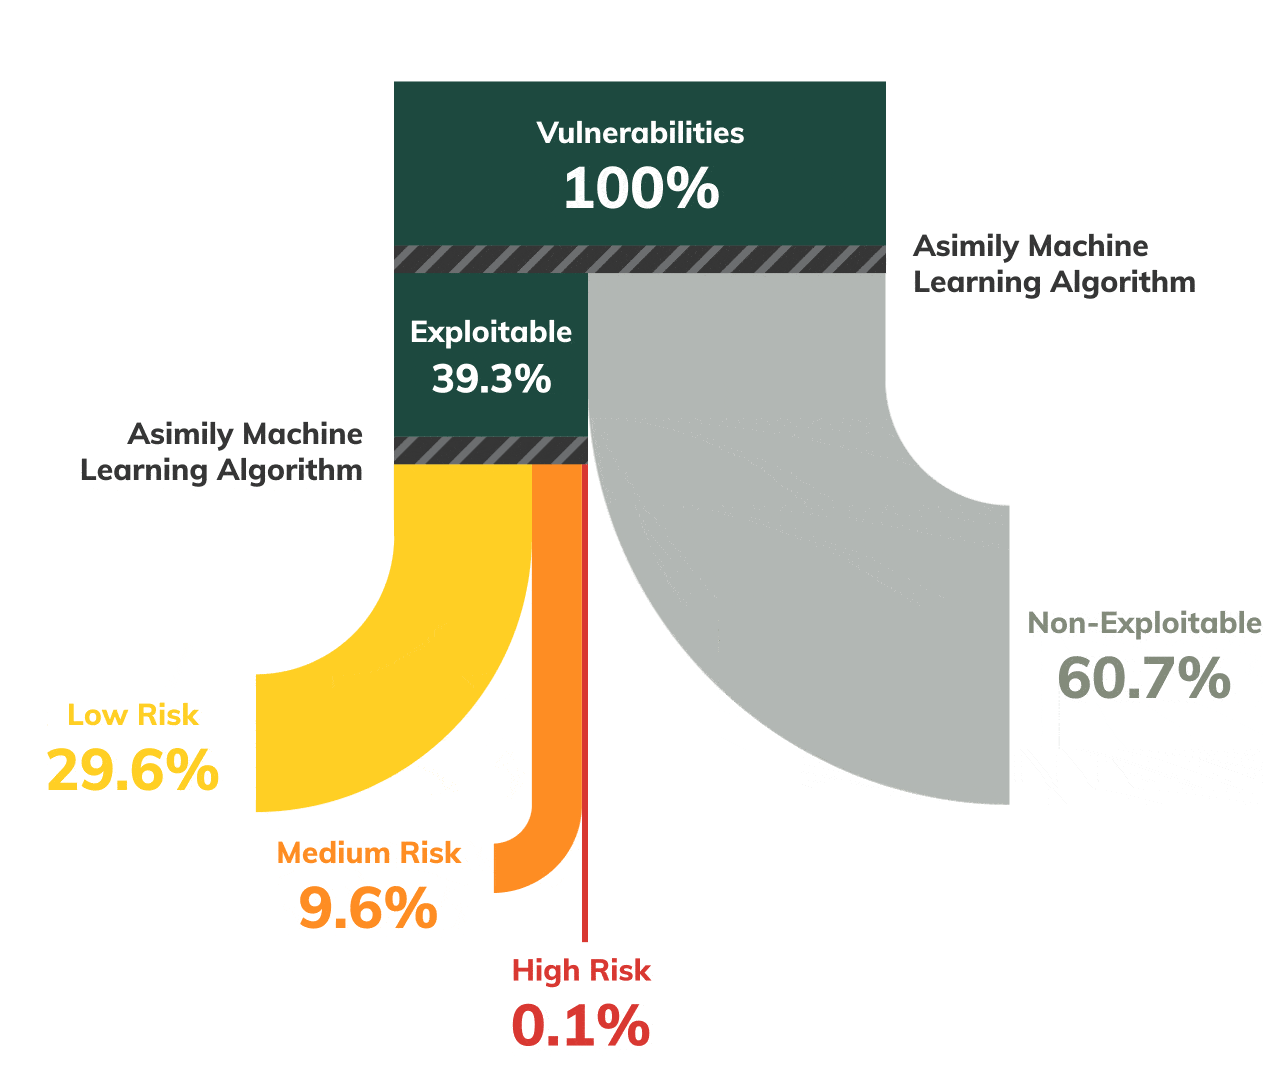
Not every CVE threatens well-configured financial infrastructure. Asimily’s ATT&CK Analysis maps vulnerabilities to your specific systems and network topology to determine what is genuinely exploitable in your environment, so teams work the exposures that could disrupt transactions or customer access rather than the thousands of CVSS alerts that will not.
Validate Changes Before Deployment
Financial system downtime is measured in thousands of dollars per minute, which leaves no room for guesswork. Policy Simulation runs a proposed policy against actual traffic and shows exactly which systems and devices would be affected before anything is applied.
Segmentation That Stays Current
Infrastructure does not hold still. Terminals are added, systems are decommissioned, and topologies shift between audits. Continuous Segmentation tracks whether policies still match the current state of the network and adapts, so enforcement does not fall out of date between reviews.
Policy in Your NAC’s Native Format
Most banks have capable NAC and firewall infrastructure that was never operationalized for segmentation. Segmentation Orchestration generates policies in the native format of Cisco ISE, Aruba ClearPass, or Arista, simulates them against live traffic, applies them, and maintains them as the network changes.

Real-Time Incident Response
When an incident does occur, native packet capture can be triggered on any device in real time. Investigators get the traffic record needed to scope the event and establish what was reached, which shortens investigation and limits blast radius.
Keep Financial Institutions, Parties, and Data Safe
Spend Time Where it Matters
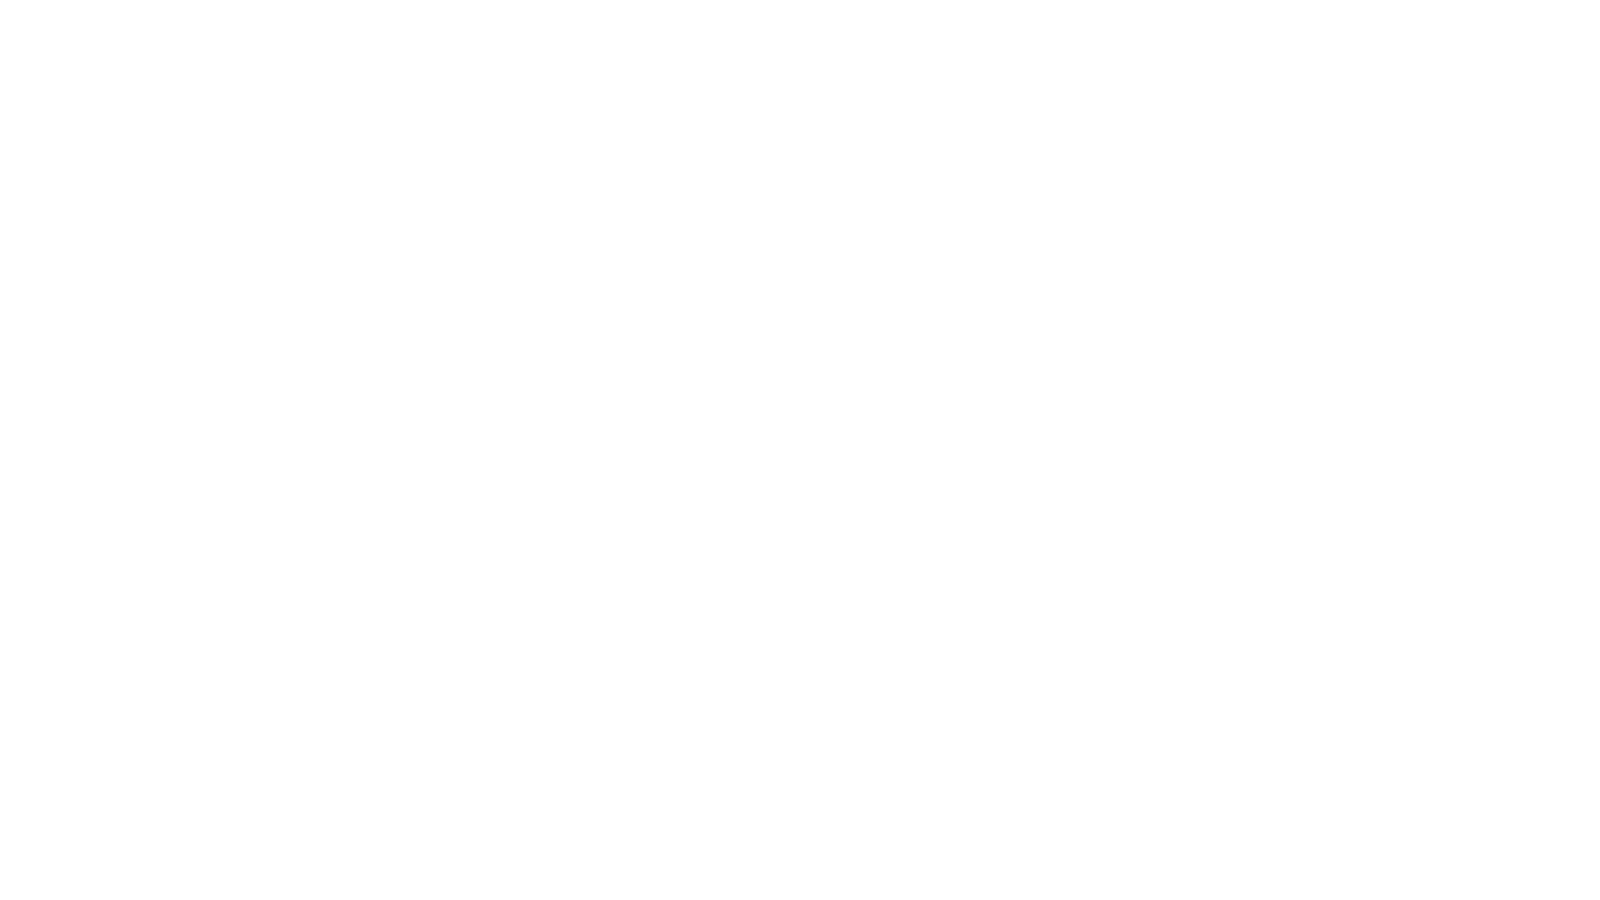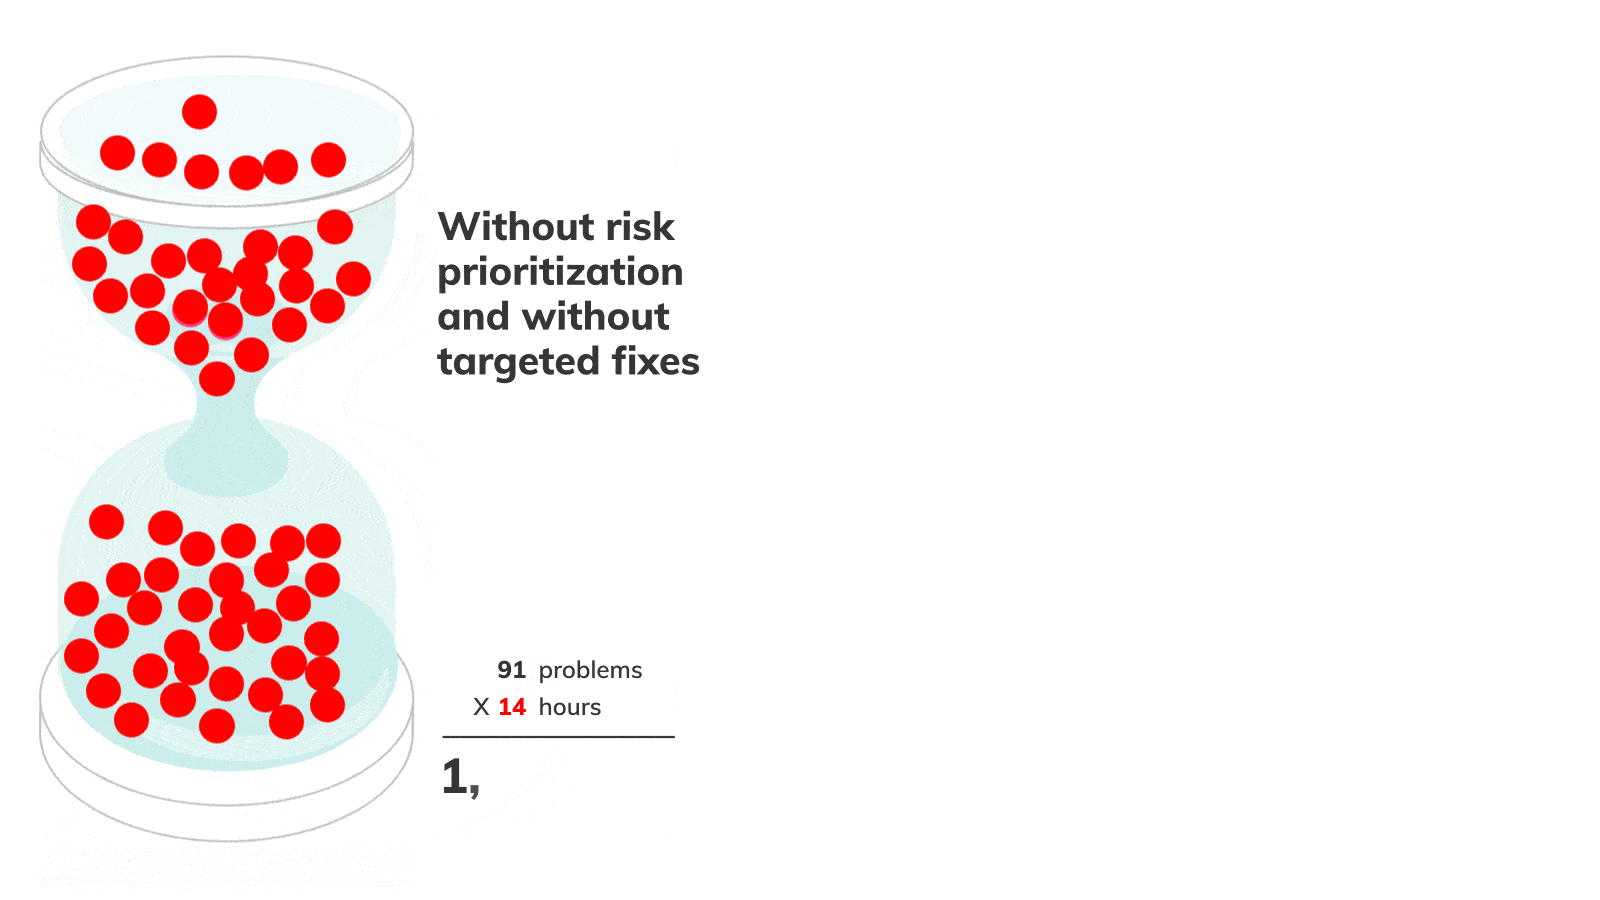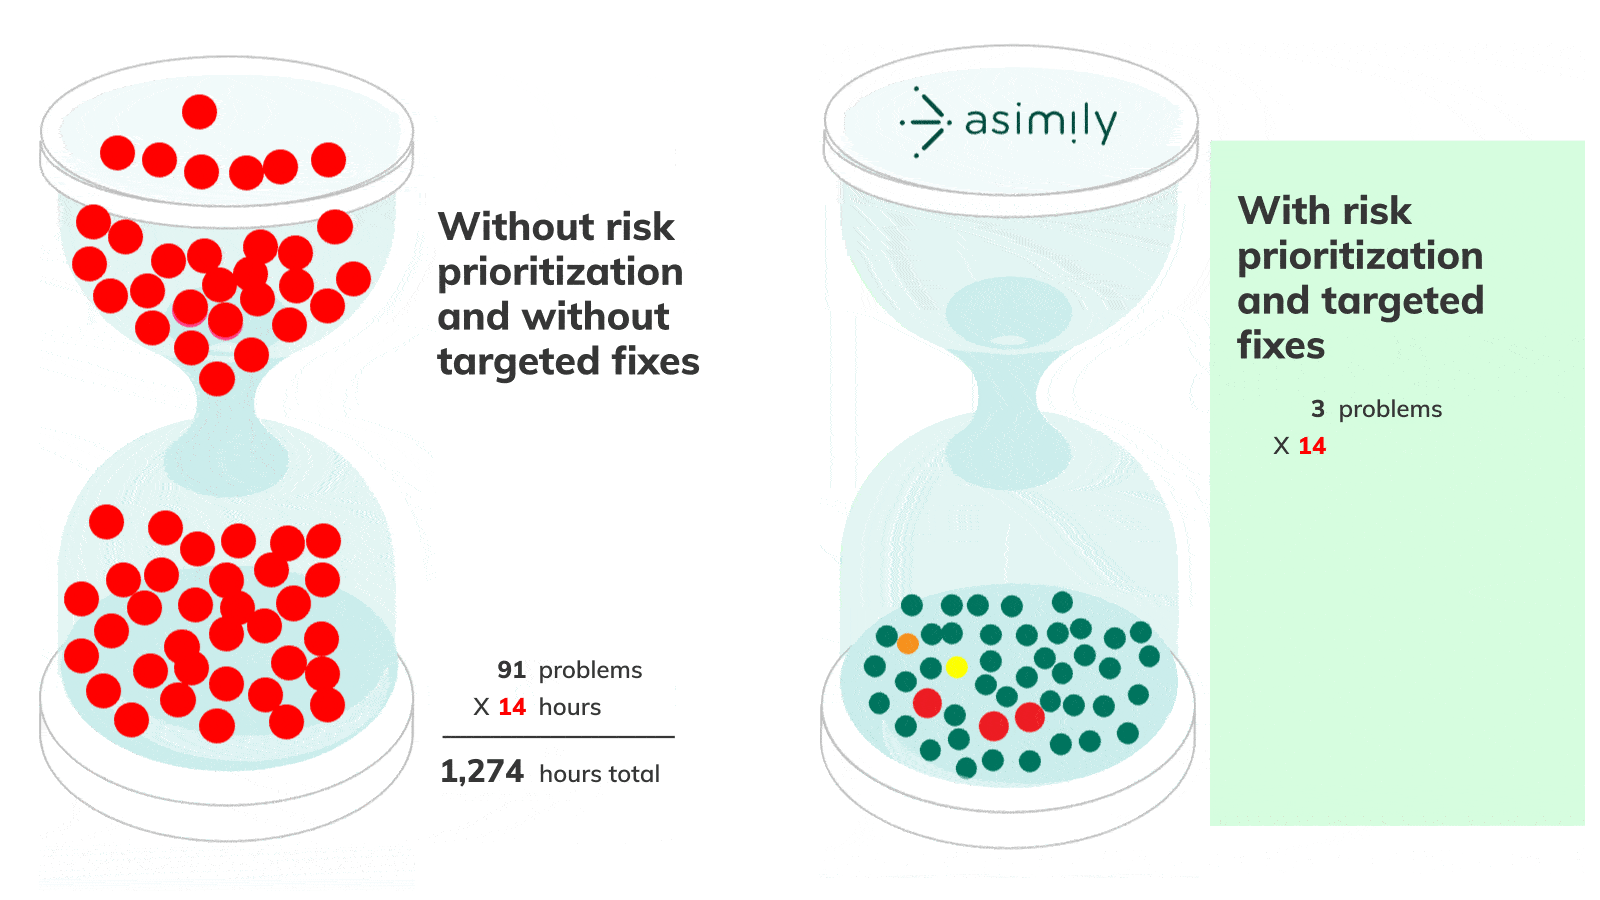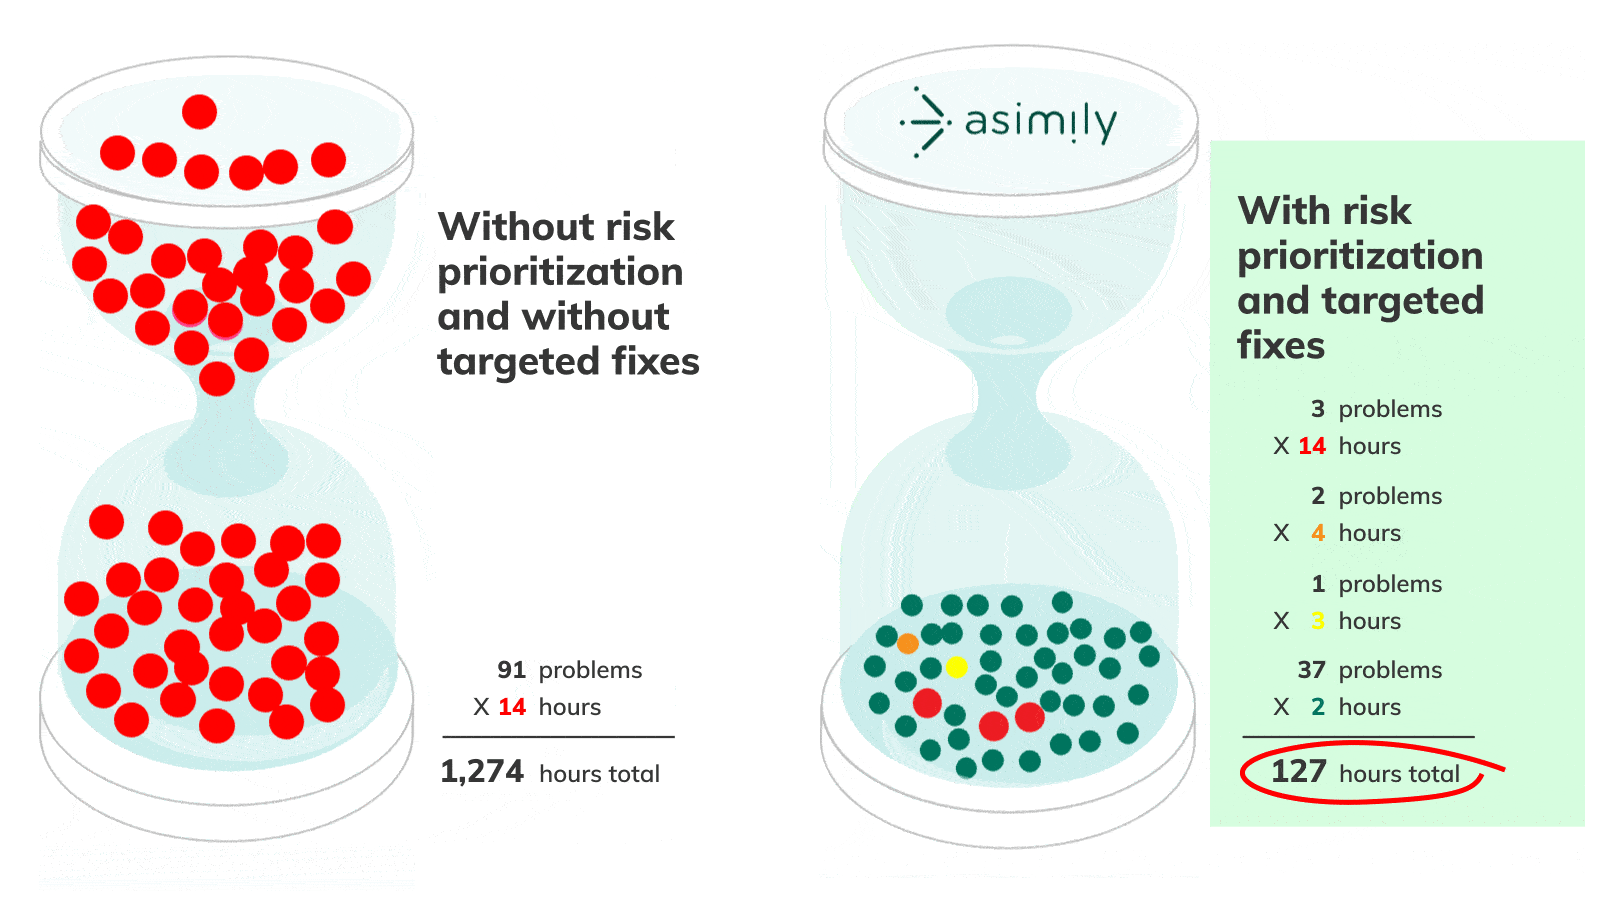
Vulnerability teams lose weeks triaging alerts that carry no real risk to operations. Asimily concentrates effort on the exposures that are exploitable against your specific infrastructure, so teams close real gaps instead of working a queue down for its own sake.
Compliance Without Gaps
PCI-DSS audits require proof of payment system protection: device inventory, vulnerability prioritization, and enforced segmentation. Asimily produces the audit trail that documents all three, along with a record of enforcement effectiveness suitable for board reviews and regulatory inquiries.

Security Without Operational Risk
Operations teams hold an effective veto over anything that risks transaction availability, and they are right to. Asimily shows the exact traffic impact of a policy against observed data before it reaches production, which turns a segmentation debate into a review of evidence.
Secure Every IoT Device.
Automatically.
Cyber threats move fast — so should you. Asimily gives instant inventory and smart, prioritized risk mitigation insights for every IoT, OT, and IoMT device — so you can take action before threats strike.


