This manufacturer had a critical blind spot: they had zero visibility into the network of devices sitting deeply behind their PLCs within lower-level cell zones (Purdue Levels 0-2). Traditional methods like configuring SPAN sessions, installing physical TAPs, or placing low-end collector boxes were not physically or architecturally feasible. After piloting other well-known OT security vendors who relied strictly on passive wire data analysis at higher network layers, they found those vendors could not see behind the primary PLCs. The child devices were invisible during these pilots.
Protect Production and Safety Without Operational Disruption
IoT, OT, and IT Security Solutions for Manufacturing
Manufacturers run production lines, PLCs, motion controllers, safety systems, and facility infrastructure across thousands of connected devices. Production downtime is measured in thousands of dollars per minute, and a safety system failure can injure workers. IT and OT teams operate separately, with priorities that rarely line up.
Request a Demo
Every new sensor, controller, and connected machine on the plant floor is also a new way in for attackers, and the bridge between corporate IT and OT is where most of that risk concentrates. Asimily watches that bridge by surfacing command and control traffic, default credentials, suspicious communications, and lateral movement pushing into ICS networks and building management systems, and by spotting configuration drift and abnormal behavior across OT protocols including Profinet, BACnet, Modbus, and CIP. Production keeps moving, and security teams contain threats well before they reach the systems that run the plant.
Request a Demo
Safeguard Your Operations Without Interrupting Them
What Asimily Does for Manufacturers
Manufacturing runs on continuous flow processes and uncommon device protocols, and most security tooling was built for neither. Asimily covers the plant floor and the corporate network on one platform, including the devices that speak protocols a conventional scanner has never seen.
See Past the PLC
Most security tools stop at the controller, which leaves the devices behind it invisible. Asimily maps production lines, PLCs, motion controllers, safety systems, and facility infrastructure in one inventory, including the child devices sitting in lower-level cell zones that SPAN sessions and passive-only tools never surface. Asimily’s discovery is agentless and safe to run against live production.
Prioritize Risk Effectively
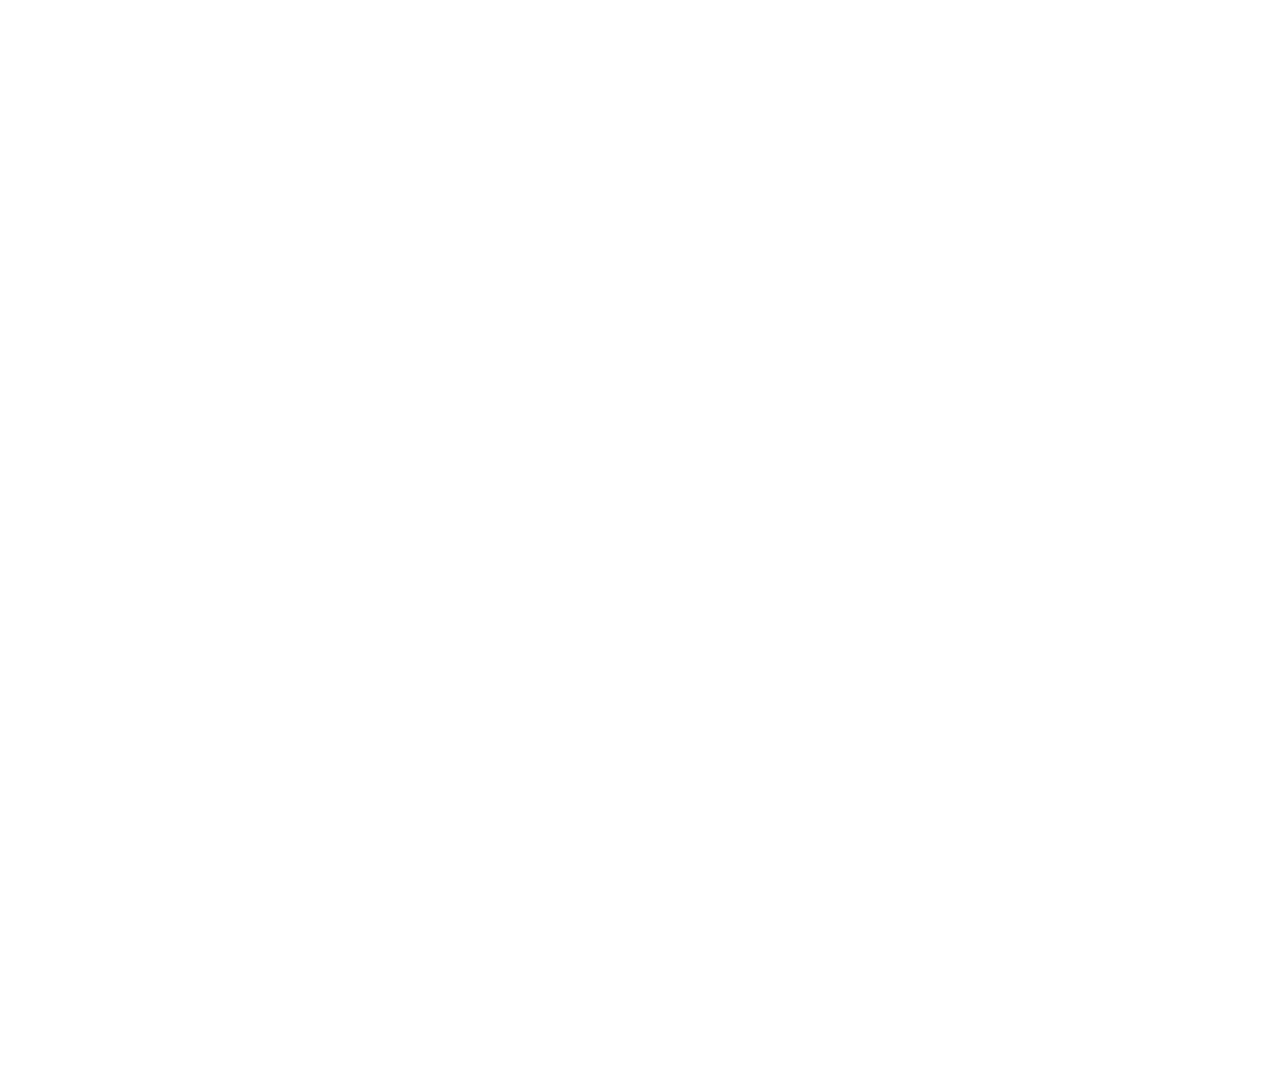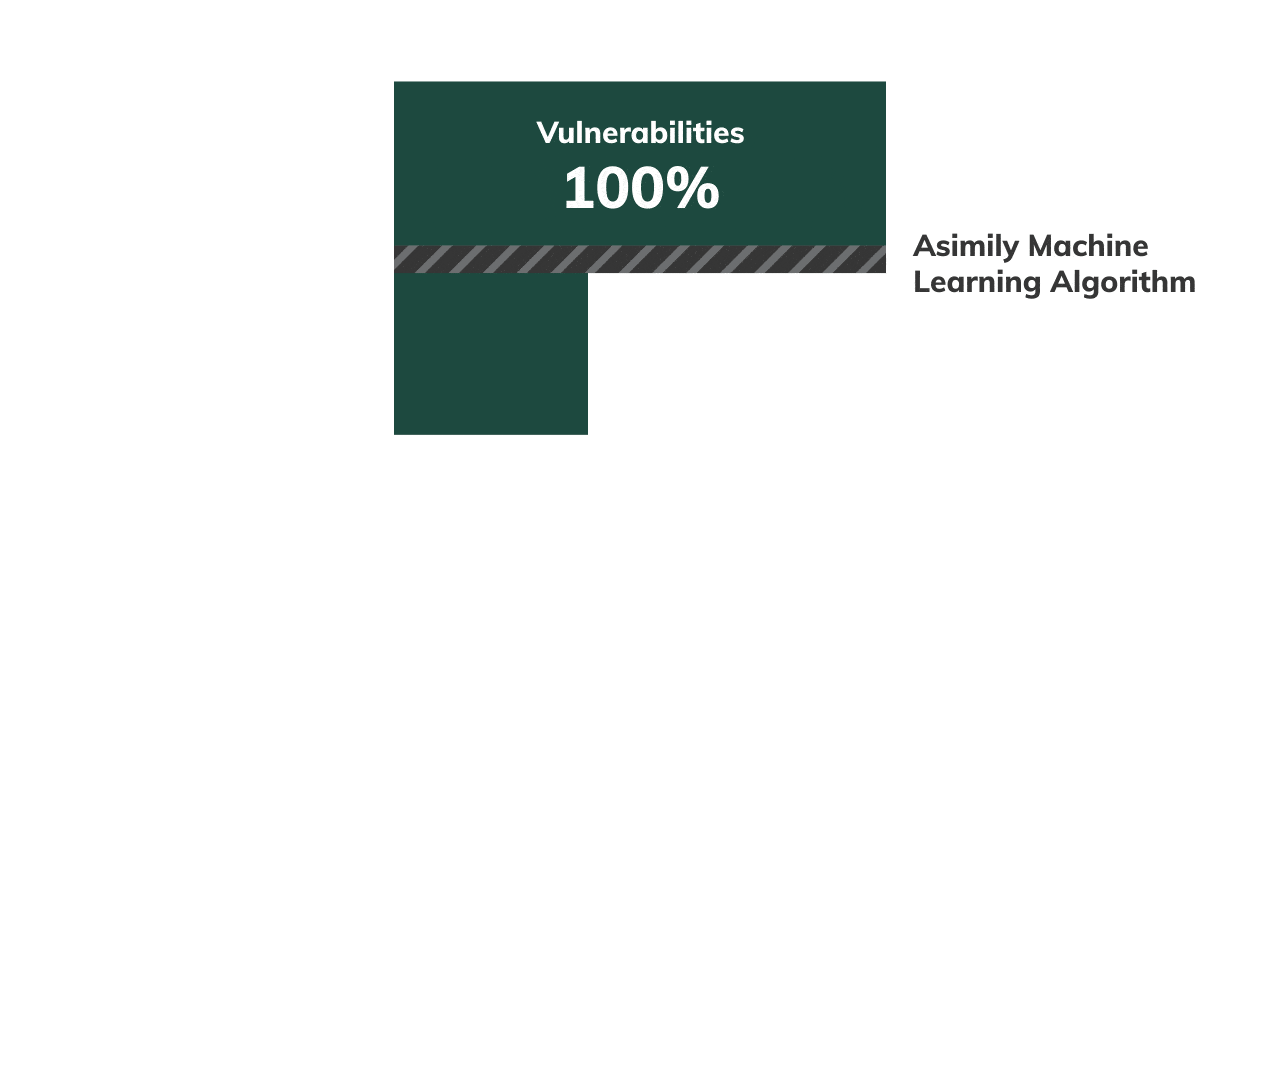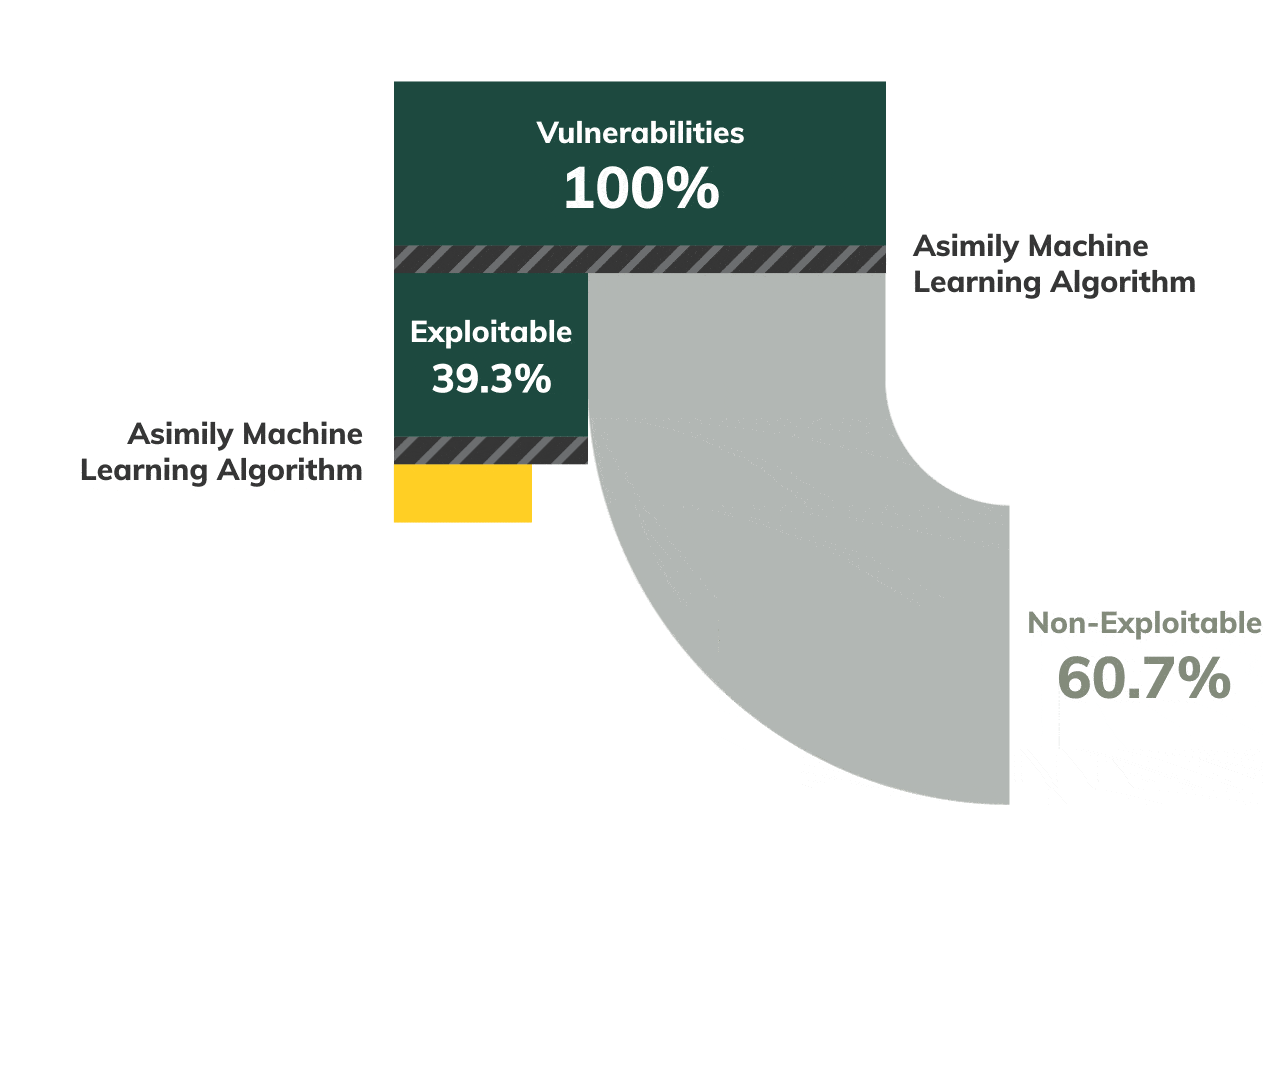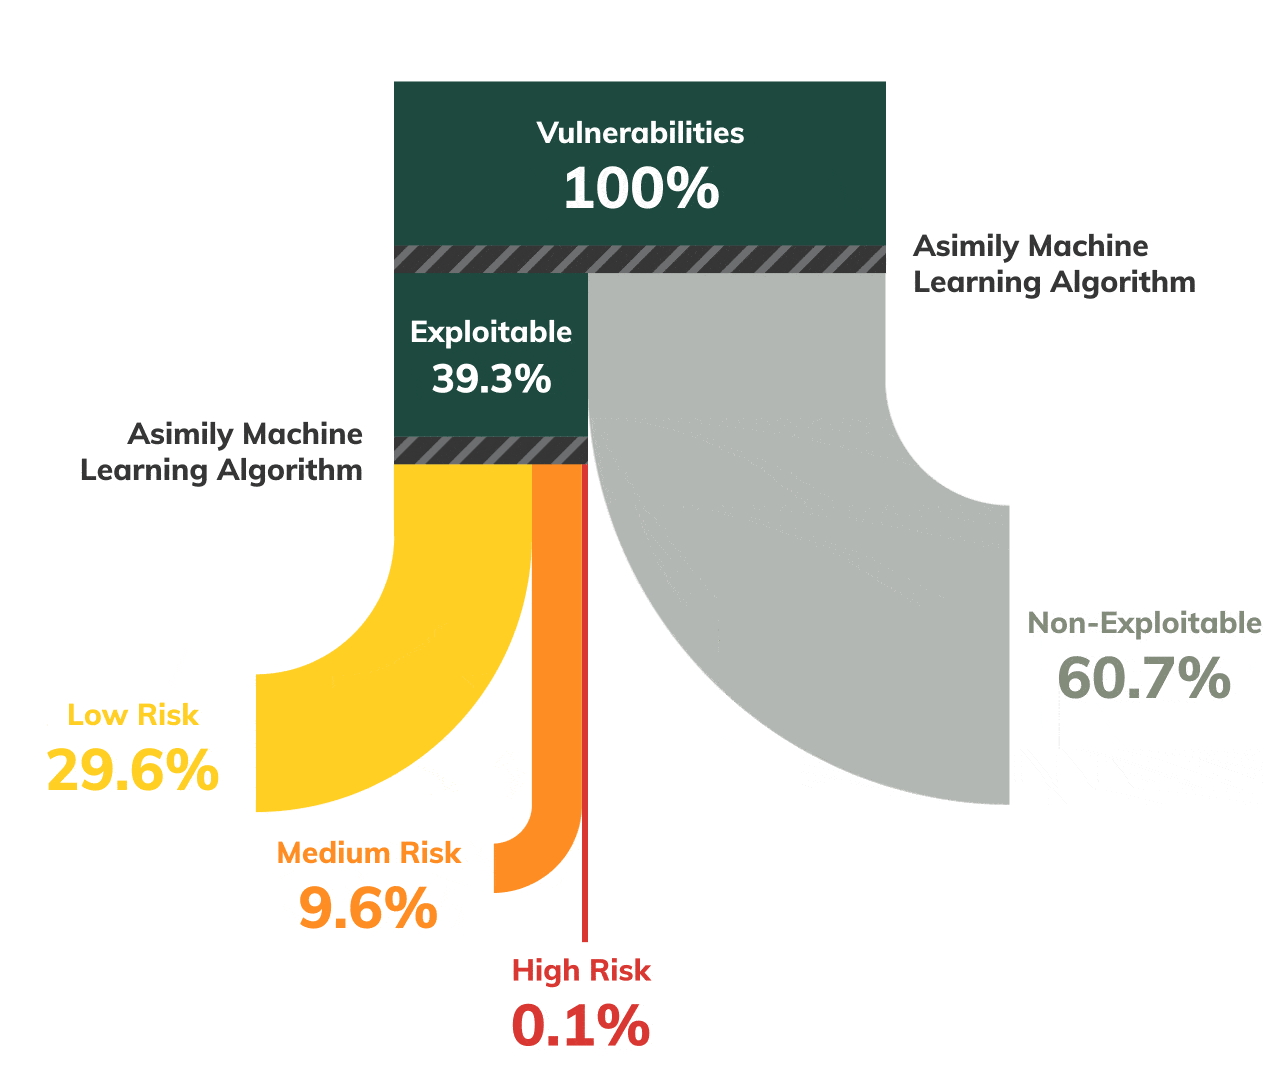
Asimily’s ATT&CK Analysis determines whether a vulnerability is genuinely exploitable on your specific equipment and topology, and custom impact factors let you weight safety and downtime the way the plant actually values them. A scarce security team gets a short list tied to production consequence rather than a CVE count.
Prove The Policy Before You Push It
Segmentation Orchestration generates policies in your NAC or firewall’s native format, and Policy Simulation runs them against real observed traffic first, showing exactly which devices and connections would be affected. Nothing reaches the floor until the impact is on the table, which is how a change gets approved by the people responsible for uptime.
Monitor Continuously
Attackers time their work for thin shifts, when an anomaly has the best chance of going unnoticed. Asimily monitors device behavior and configuration drift continuously across OT protocols, and native packet capture can be triggered on any device, so containment starts with evidence rather than a reconstruction.

Protect Production, Operations, and the People on the Plant Floor
Security Without Downtime
Production managers hold an effective veto over any change that could stop a line, and they have earned it. Asimily shows the exact traffic impact of a policy against observed data before it is applied, so a segmentation proposal arrives as evidence rather than a request for trust, and IT and OT stop negotiating in the dark.

Compliance for Manufacturers
Manufacturing is audited on evidence that controls exist and work: a current device inventory, a documented risk assessment, and proof of which policies are enforced where. Asimily produces that record continuously, so an audit request is answered from a system rather than assembled across IT and OT by hand.

Prioritize Exploitable Risk
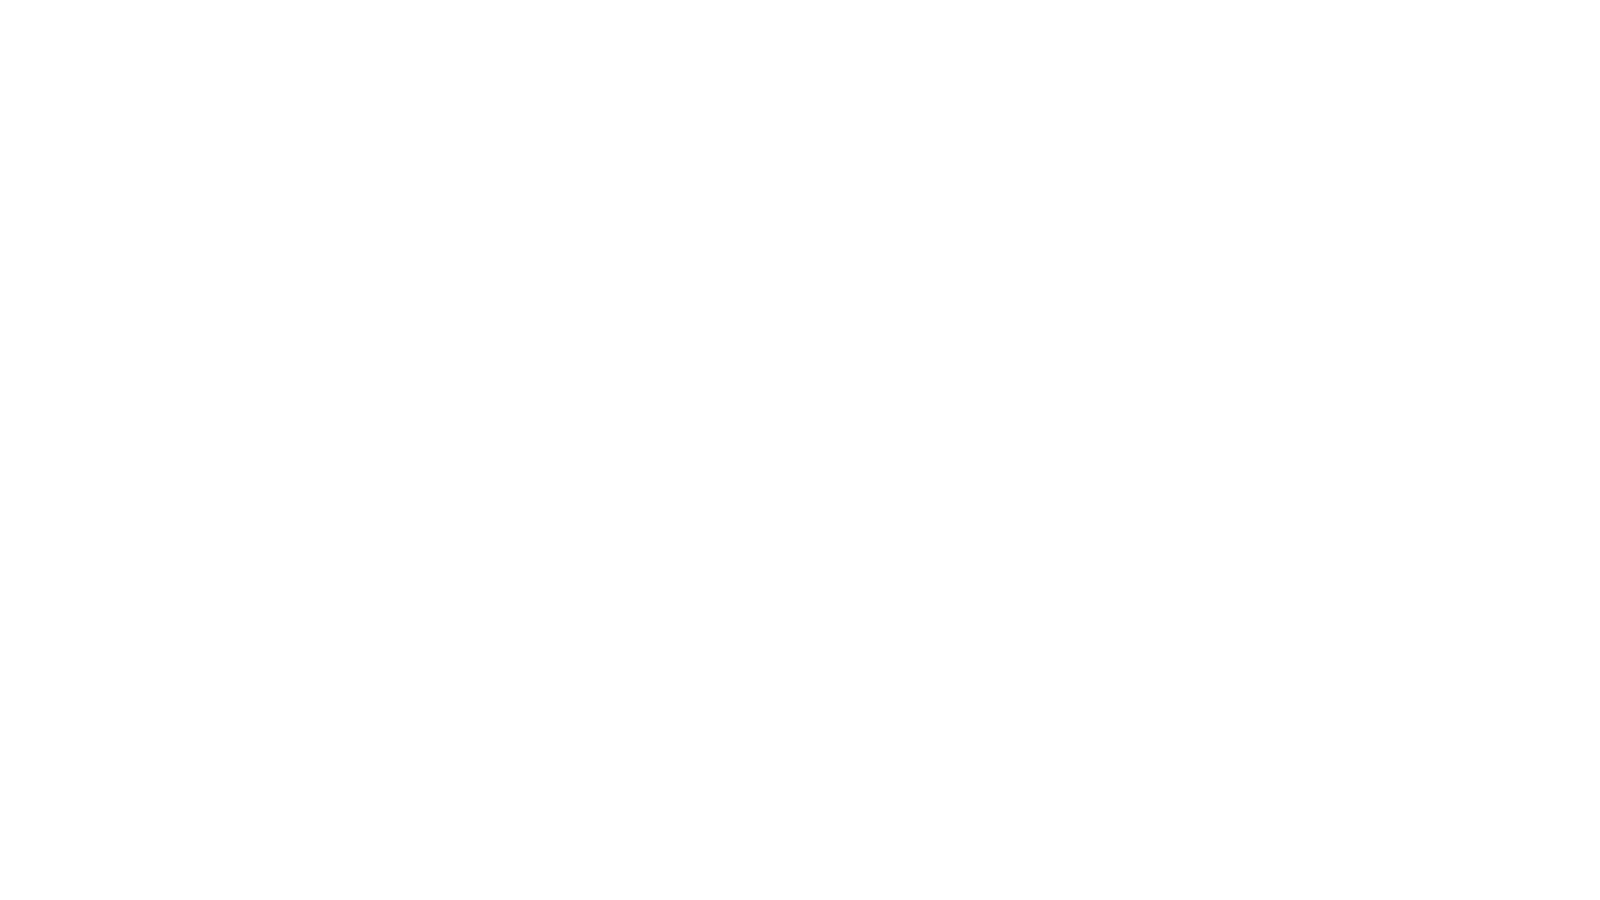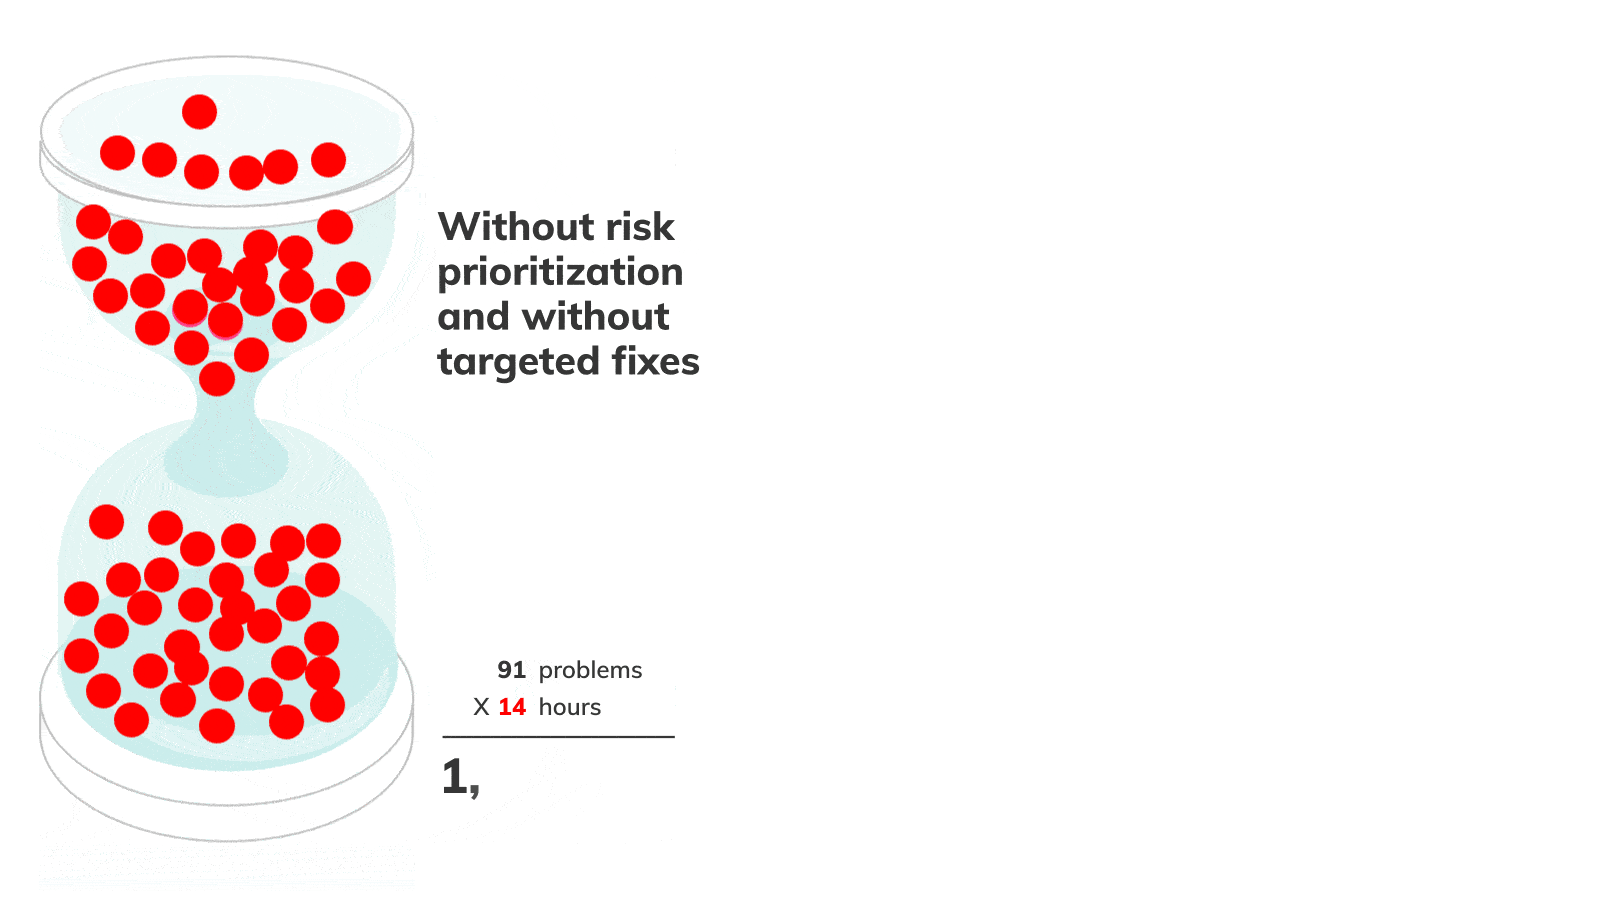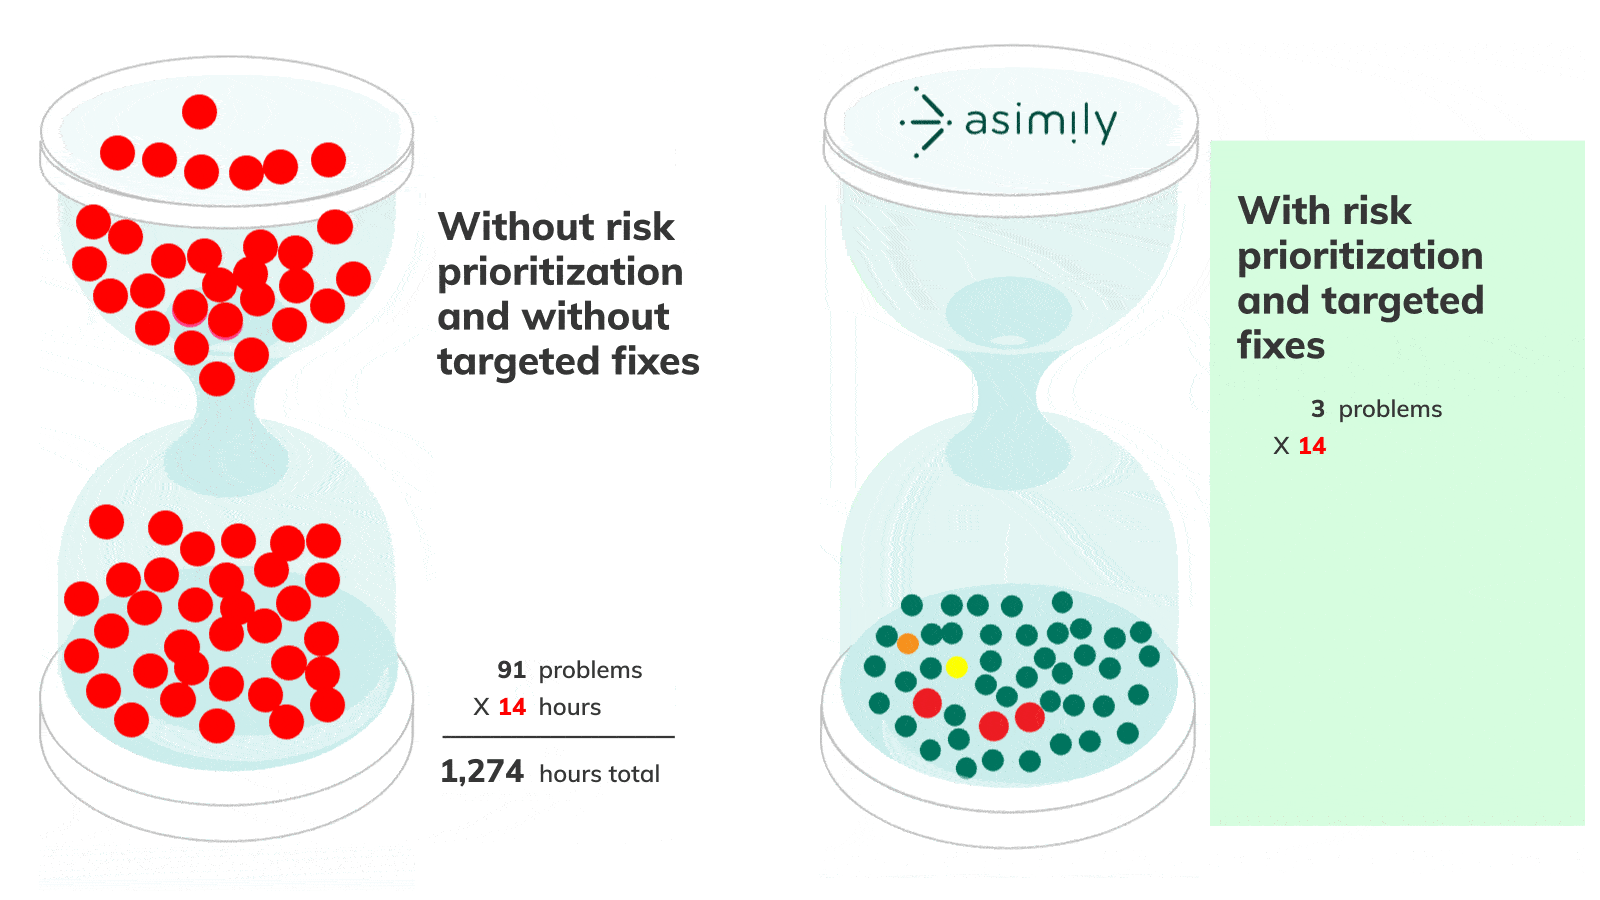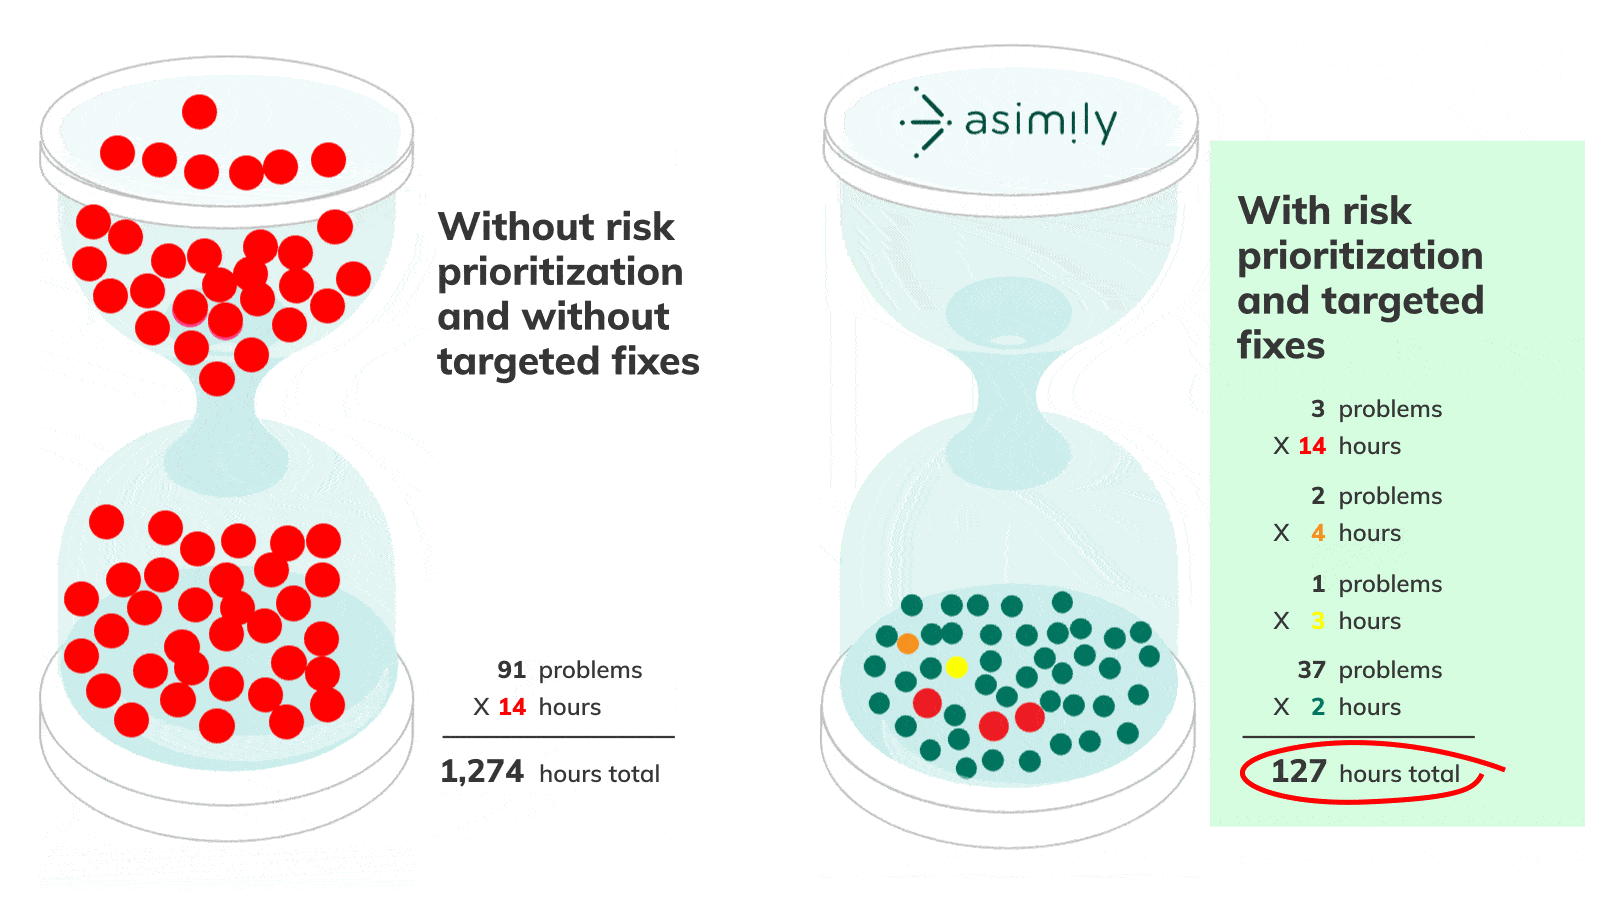
Asimily returns a risk-ranked set of devices with a specific action attached to each one, so the team works from a short list of decisions rather than a long list of findings. The fixes that reduce the most risk are usually the ones that fit inside a maintenance window you already have.
Use Resources Efficiently
A controller that still runs the line does not get replaced because its vendor stopped issuing patches. Asimily identifies targeted mitigations that close the exposure on equipment past vendor support, so a security gap never becomes an unplanned capital request or an unscheduled line stoppage.
Secure Every IoT Device.
Automatically.
Cyber threats move fast — so should you. Asimily gives instant inventory and smart, prioritized risk mitigation insights for every IoT, OT, and IoMT device — so you can take action before threats strike.


